
 Compliance, NCSC, Technical Mapping
NCSC Offline Backups Control Module Mapping Guide
A technical mapping of Control by Firevault modules to the NCSC guidance 'Offline backups in an online world'. Each of the four published rules, the architectural answer, the modules involved and the evidence a UK auditor will ask for.
4
NCSC rules for offline backups, mapped in full below
9
Control by Firevault modules named in the mapping
Layer 1
Where the disconnection happens, below the network
The NCSC Threat Model Assumes The Attacker Is Already Inside
The National Cyber Security Centre publishes 'Offline backups in an online world' freely at ncsc.gov.uk. Its premise is stark: plan for an attacker who already holds the production estate, including the credentials and tooling that reach ordinary backups. The only copy that survives is one the attacker cannot reach at all. Offline Secure Storage® is built around that same threat model, and Control by Firevault governs the physical path to it. NCSC does not certify products, so this guide is a mapping, not a certification claim.
This is a mapping, not a certification claim. Firevault holds Cyber Essentials Plus. Everything else on this page is stated as alignment: Offline Secure Storage® produces evidence you can point at in your own submission, assessment or audit.
- 4: NCSC rules for offline backups, mapped in full below. Source: NCSC, Offline backups in an online world
The Four NCSC Rules, In The Published Order
Each line below is something an assessor, regulator or underwriter can ask you to evidence.
The offline rule: at any given time, one or more backups are offline
The recovery rule: data in backups is restorable and recoverable to a known-good state
The 3-2-1 rule: critical data is saved in multiple backup locations
The regular rule: critical data is backed up regularly and recovery is tested
Where A Typical Backup Estate Fails The Rules
What happens when the control is missing, and the record cannot be produced.
Every Copy Stays Reachable
Backup servers, snapshots and cloud replicas all hold standing network paths. An attacker with the estate reaches all of them at once.
One Identity System Guards Everything
When backup administration shares the production directory, a single privileged compromise opens the backup too.
Recovery Is Assumed, Not Tested
The NCSC regular rule expects tested restoration. Most estates discover a broken backup only during the incident.
3-2-1 Without An Offline Copy
Three copies on two devices with one offsite still leaves every copy online. The NCSC guidance is explicit that 3-2-1 alone is not enough.
The Control Modules Behind Each Answer
Control by Firevault is the platform that governs when the physical path to Offline Secure Storage opens, who may open it and what happens while it is open. These are the modules the mapping relies on.
“The NCSC guidance describes a copy the attacker cannot reach. We build exactly that copy, and the modules below are how it stays that way.”
Mark Fermor, CTO, CMO & Founder, Firevault
Evidence The Mapping Produces
The records most often moved into Offline Secure Storage® for this framework.
Logged connection windows with identity verification
Checksum verification records for each test
Partial restore evidence from the offline copy
Version history proving known-good states survive
Jurisdiction and custody records for the offsite copy
Audit packages for insurers, auditors and the board
Read the full rule-by-rule mapping
The alignment section below pairs each NCSC rule with the architectural answer and the exact modules involved.
Pairs with the on-premises principles
The same architecture maps to the six NCSC principles for ransomware-resistant on-premises backups.
Alignment, not certification
NCSC does not certify products or endorse suppliers. Firevault maps its architecture to the published guidance and hands over the evidence.
Built for UK compliance queries
The mapping gives UK organisations the language to answer auditors, insurers and boards in the NCSC's own terms.
Tell us which framework you are being tested against.
We will map Offline Secure Storage® to the outcomes your assessor is checking, and give you the wording and evidence to submit.
From £360 a month including VAT. 36-month commitment. First payment at checkout.
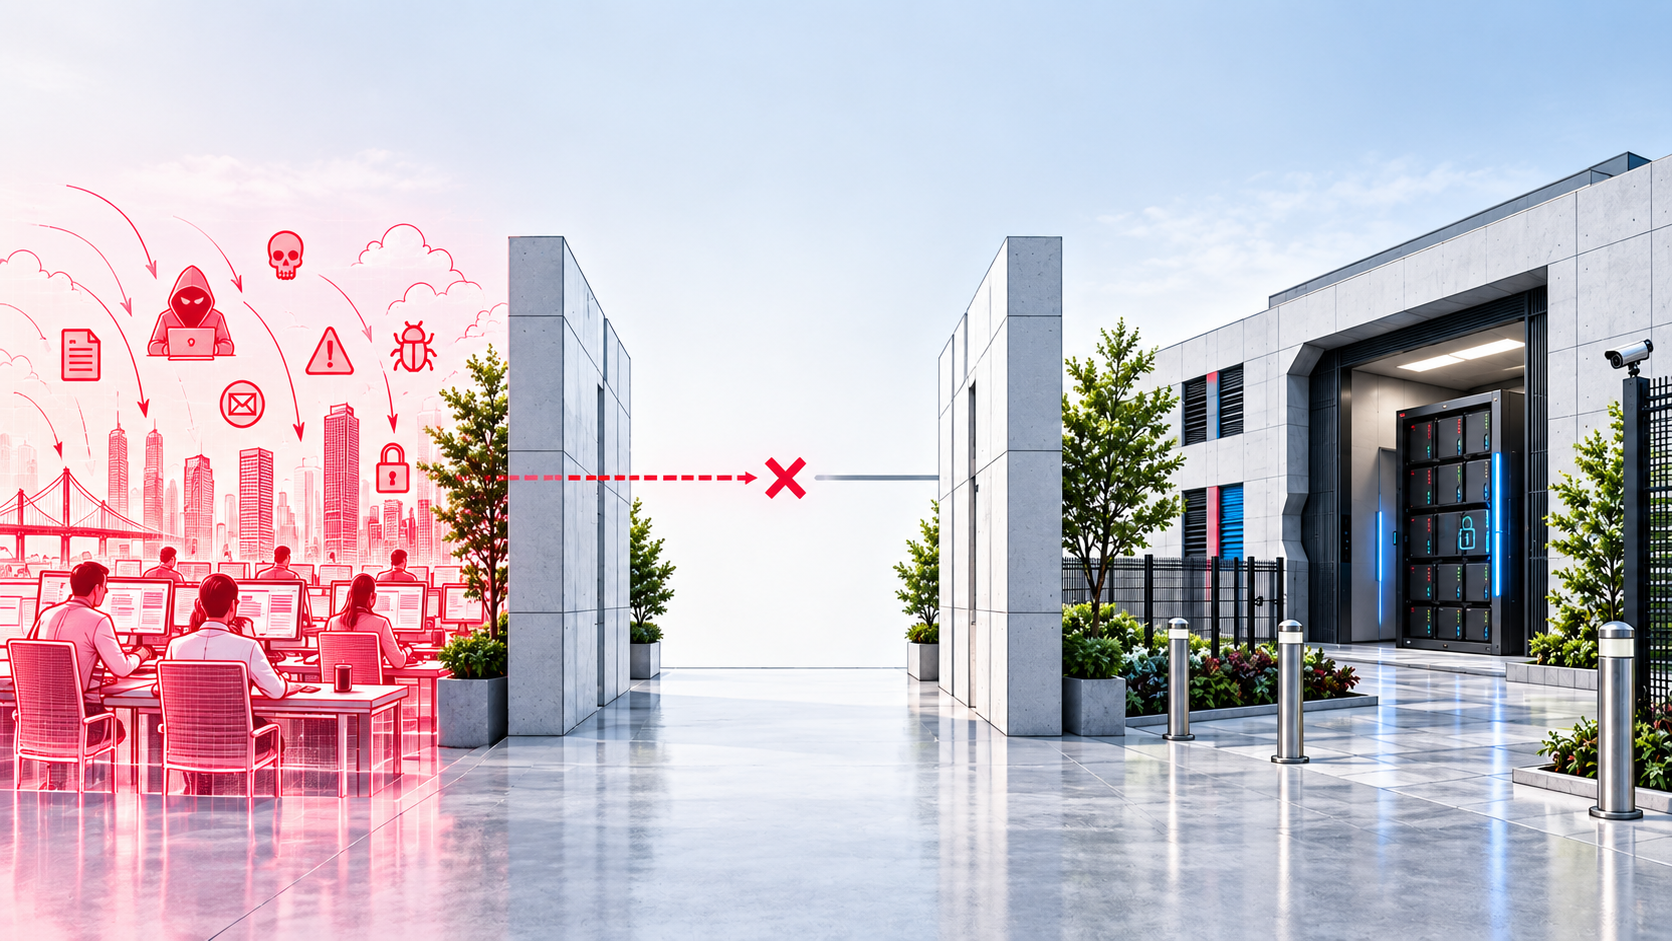
The connection, physically closed
On one side, the production estate with an attacker already inside. On the other, the offline copy behind a physically closed connection. Between them, no path: no interface, no address and no route to follow.
The nine Control by Firevault modules
The offline rule is met by Offline Secure Storage® itself. The offline copy is physically disconnected by default and stays closed between scheduled windows: no interface, no address and no route exist for an attacker inside the production estate to follow. Control by Firevault governs when a window opens, who may open it and what is logged. These are the nine modules, with their official platform icons.
Fracture
FIRE layer
Break a selected network path when an authorised incident response calls for physical separation.
Isolate
FIRE layer
Control both sides of a protected intermediate zone, rather than relying on a single network crossing.
Relay
FIRE layer
Stage approved connectivity between public, intermediate and private zones, without leaving an open end-to-end route.
Execute
FIRE layer
Give designated decision-makers a defined higher-priority way to change a selected connection state.
Validate
VAULT layer
Require two independent approvals for the same proposed connection change before it is released.
Array
VAULT layer
Protect a named critical asset through multiple assessed, diode-protected connection boundaries.
Unlink
VAULT layer
Physically withdraw selected access paths so critical systems are not continuously reachable through them.
Lock
VAULT layer
Allow selected connections only during approved time windows, with defined expiry and closure behaviour.
Transfer
VAULT layer
Control when a designated connection around a separately enforced one-way data path is available.
NCSC blog post, offline backups in an online world
Mapped to the NCSC rules for offline backups
The National Cyber Security Centre publishes its guidance Offline backups in an online world freely at ncsc.gov.uk. It sets out what an offline copy must do to survive an attacker who already holds the production estate. Offline Secure Storage® is built around that same threat model. The four published rules below are paraphrased and paired with the Firevault architectural answer, in the NCSC order.
NCSC rule, paraphrased
The offline rule
At any given time, are one or more backups offline?
Only connect a backup to live systems when necessary, and never have every backup connected at the same time.
How Offline Secure Storage answers it
Offline Secure Storage® automates the offline state at Layer 1. The gold copy has no active interface or address between separately controlled, identity-verified connection windows.
Control by Firevault modules
- Unlink
- Relay
- Lock
NCSC rule, paraphrased
The recovery rule
Is the data in cloud backups restorable and recoverable?
Keep the ability to return to a known-good state if ransomware reaches a backup.
How Offline Secure Storage answers it
Controlled restore windows allow an authorised recovery from the offline copy. Verification and restore events are logged before the physical path closes again.
Control by Firevault modules
- Validate
- Relay
- Array
NCSC rule, paraphrased
The 3-2-1 rule
Is critical data saved in multiple backup locations?
Keep at least three copies, on two devices, with one copy offsite, while recognising that 3-2-1 alone does not require an offline copy.
How Offline Secure Storage answers it
Firevault supplies the genuinely offline copy of last resort alongside operational and immutable backups. It is held in a carefully selected bunker in the customer's chosen jurisdiction.
Control by Firevault modules
- Array
- Transfer
- Isolate
NCSC rule, paraphrased
The regular rule
Is critical data backed up regularly?
Create backups regularly and test them to confirm that recovery works as expected.
How Offline Secure Storage answers it
Recurring verification windows bring the copy online, checksum-verify the data, restore in part and disconnect again. Every test is a logged event.
Control by Firevault modules
- Execute
- Validate
- Array
Alignment, not certification
NCSC does not certify products or endorse suppliers. Firevault maps its architecture to the published blog post and hands over the connection and restore evidence, so a UK organisation can make the case to its own auditors, insurers and board.