 Knowledge Vault
Understand the risk. Find the control.
Welcome to our knowledge vault, where you will find content and insight: research, incident analysis, practical guides for protecting data and systems that should not remain continuously reachable.
Start with the issue in front of you.
Choose the problem you need to understand. We will take you straight to the most relevant analysis, guidance and controls.
What matters now
The incidents and decisions shaping cyber resilience now, selected for leaders who need the consequence as well as the headline.

GhostAction returns: about 1,900 GitHub accounts used to target more than 30,000 repositories
A renewed GhostAction wave pushed malicious GitHub Actions workflows to more than 30,000 repositories and tried to extract 3,174 secrets. Old, unrotated credentials did much of the work.
EY data breach: client tax records exposed through a support platform
Client tax documents held in EY support tickets were downloaded by an unauthorised third party. Later reports link the exposure to Goldman Sachs, Man Group and Tishman Speyer.
ASOS data breach: stolen customer profiles and a hijacked app notification
ASOS confirms customer-data exposure after attackers hijacked its app notifications. What happened, what was taken and why a stolen login can put more than contact details at risk.
Find the knowledge by need
Follow the decision in front of you: understand the risk, decide what belongs offline, determine where access should stop, then evidence the governance.
What is the risk?
Breaches, threat analysis, exposure patterns and evidence explaining where connected systems fail.
Explore risk and incidentsWhat data should be offline?
Guidance on crown jewels, backups, intellectual property, personal data and long-term digital assets.
Explore #OSS guidanceWhere should access stop?
Control blueprints for networks, OT, AI, remote access and systems where a path needs to be physically governed.
Explore Control BlueprintsWhat does good governance look like?
Board, regulatory and operational guidance covering resilience, accountability, recovery and evidence.
Explore governancePlaybooks and control blueprints
The long-form work: sector playbooks and control blueprints written for the people who have to sign them off.
View all playbooks Playbook
Motorsport: 2026 Playbook
Protect competitive data and control race-weekend, supplier and factory network access.
Read it28 pages · 20 min read Playbook
The Leaders' Playbook
A board-level briefing on sovereign data, succession resilience and physical protection.
Read it28 pages · 18 min read Playbook
Control for Water: Deployment Playbook
Firebreak path control, the wider Control modules and offline recovery copies, mapped to the Purdue model for water operators.
Read it28 pages · 22 min read Playbook
A Control Blueprint for AI: 2026 Playbook
40-page blueprint on AI infrastructure, open weights, agents and kill-switch design.
Read it40 pages · 28 min read Playbook
Close the File. Protect the Record.
File closure, retained records and offline custody for UK law firms.
Read it28 pages · 20 min read Playbook
A Control Blueprint for Aerospace & Aviation
Communication registers, operational states and rapid isolation for aerospace and aviation.
Read it28 pages · 22 min readLatest analysis
Search or filter above to narrow the library by the question you need to answer.
Threat IntelligenceGhostAction returns: about 1,900 GitHub accounts used to target more than 30,000 repositoriesA renewed GhostAction wave pushed malicious GitHub Actions workflows to more than 30,000 repositories and tried to extract 3,174 secrets. Old, unrotated credentials did much of the work.16 Oct 2026 · 4 minBreach AnalysisData TheftThird-Party RiskEY data breach: client tax records exposed through a support platformClient tax documents held in EY support tickets were downloaded by an unauthorised third party. Later reports link the exposure to Goldman Sachs, Man Group and Tishman Speyer.15 Oct 2026 · 7 minBreach AnalysisData TheftASOS data breach: stolen customer profiles and a hijacked app notificationASOS confirms customer-data exposure after attackers hijacked its app notifications. What happened, what was taken and why a stolen login can put more than contact details at risk.12 Oct 2026 · 14 min WhitepaperThird-Party RiskMotorsport: 2026 PlaybookProtect competitive data and control race-weekend, supplier and factory network access.10 Oct 2026 · 20 min
 Myth BustersBackup & RecoveryMyth Buster: "We already have an offline backup, so we already have Offline Secure Storage"An offline backup is good practice, but the copy is only part of the answer. The operating model must also control who reconnects it, how access is verified, what is recorded and how the path is removed again.9 Oct 2026 · 13 min
 GuideBackup & RecoveryDo we need Offline Secure Storage?Before adding another control, establish the failure scenario you are trying to remain protected from. Many organisations already have strong backup, immutability, replication and tested recovery. The real question is whether any information still needs to stay separated from the environment the organisation normally depends upon.1 Oct 2026 · 5 min
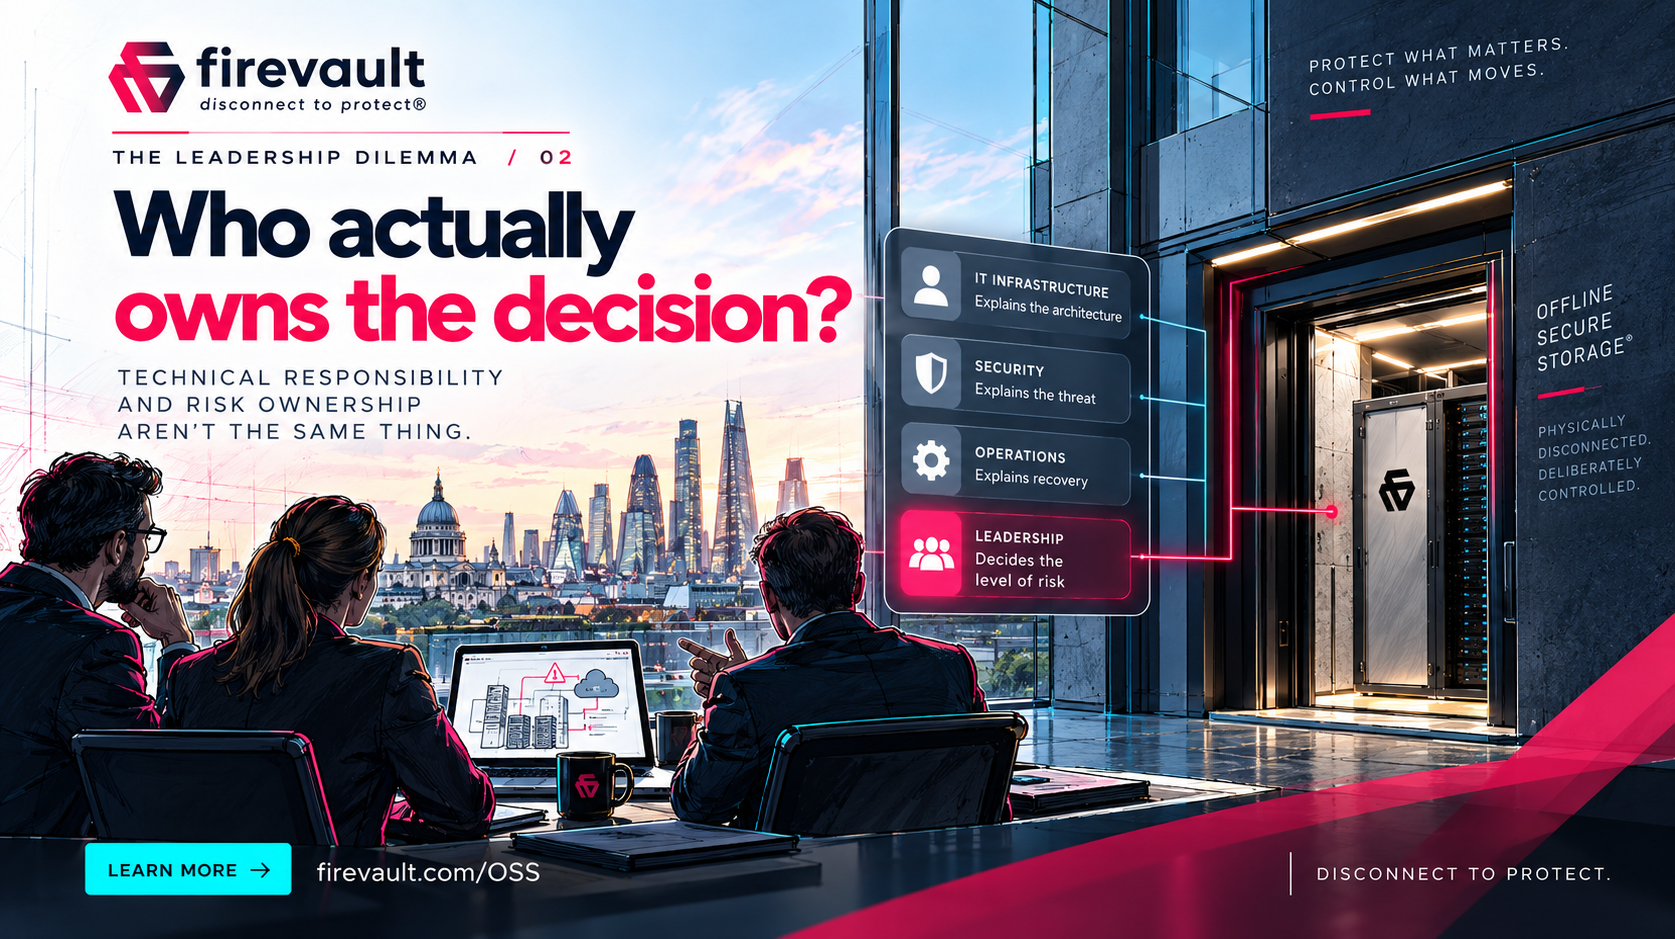 InsightBackup & RecoveryWho actually owns the decision?IT can explain the architecture. Security can explain the threat. Infrastructure can explain backup and recovery. Deciding how much residual risk the organisation is prepared to carry is a business decision, and it needs an owner.1 Oct 2026 · 3 min
 Breach AnalysisData TheftCyber DisruptionDyfed-Powys Police confirms cyber attack as staff information may have been compromisedDyfed-Powys Police has confirmed that a cyber attack identified on 14 September disrupted non-emergency systems and may have exposed staff information. The force says it has found no evidence that public data was accessed.25 Sept 2026 · 3 min
Turn research into resilience
You have read the evidence. Now see how offline secure storage protects your most critical data from every threat analysed above.
From £360 a month including VAT. 36-month commitment. First payment at checkout.