
News
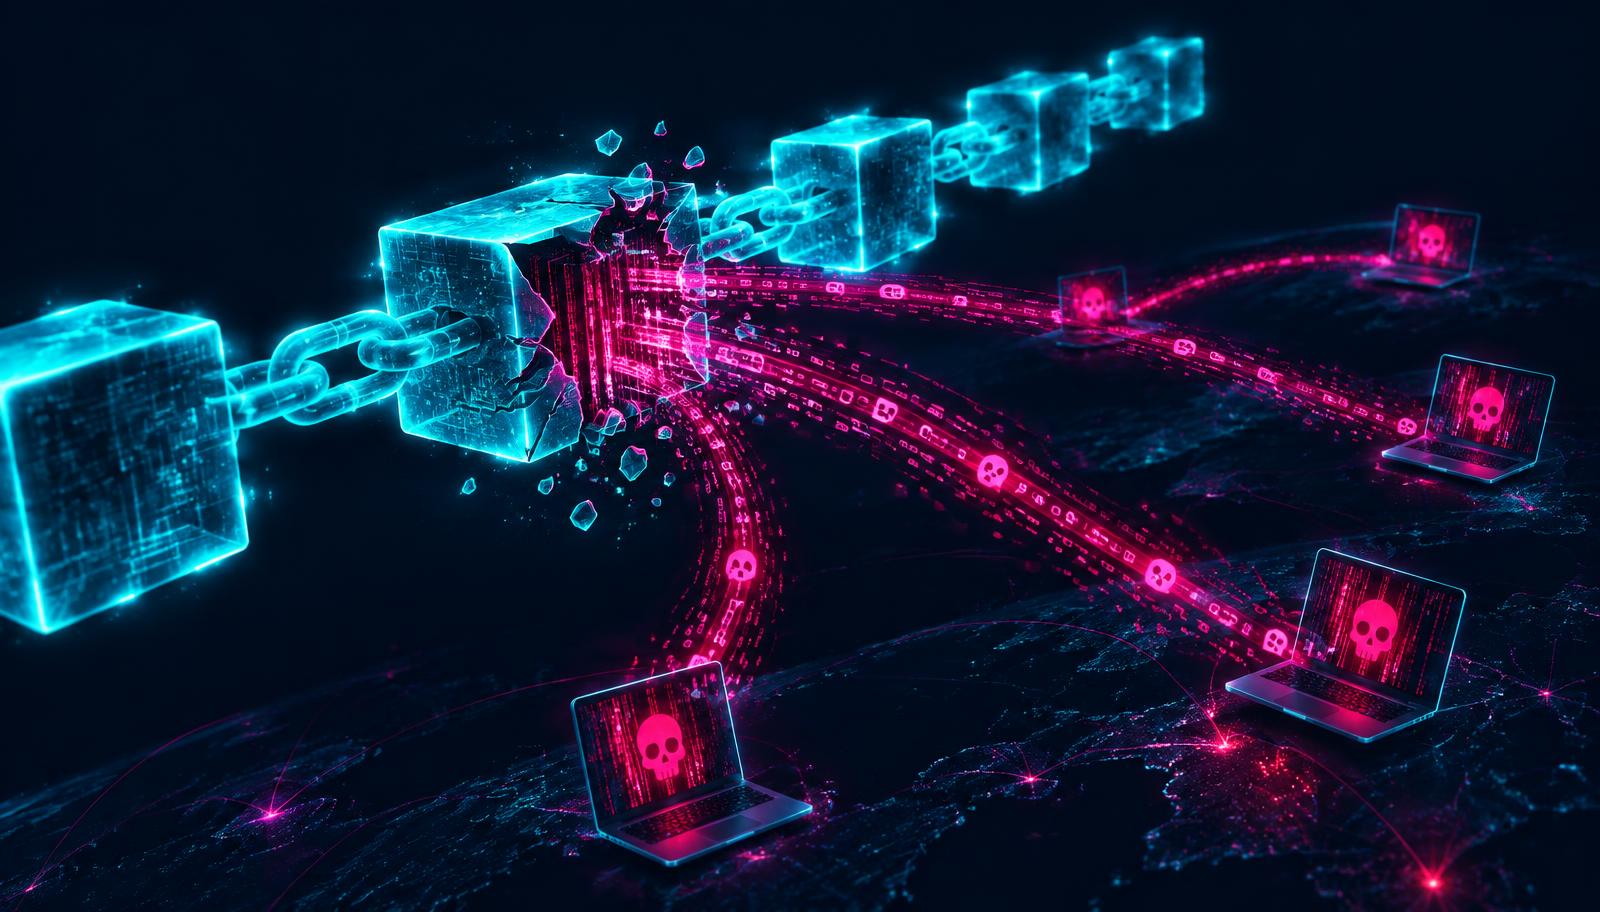
Blockchain dead drops surge 440% as North Korea and Iran hide malware on public ledgers
Chainalysis research shows malicious blockchain writes rising from 2.06 to 11.1 a day in under a year, with state-linked groups now behind most new activity. Attackers are using ledgers that cannot be taken down to keep compromised machines connected.
Mark FermorCTO, CMO and Founder, Firevault
Published 24 September 2026 · 3 min read
What the research found
Research published by blockchain analytics firm Chainalysis on 17 September 2026 shows a 440% year-on-year rise in what it calls blockchain dead drops (BDD). In these schemes, attackers write malware instructions, command-and-control (C2) addresses or pointers into public blockchain transactions and smart contracts, where infected devices can look them up on demand.
The average number of malicious blockchain writes rose from 2.06 a day to 11.1 a day in less than a year. Chainalysis links the acceleration to the release of high-capacity open-weight Chinese AI models that place no restrictions on generating malicious code, although it notes that its measurement shows correlation rather than proof of cause.
State actors now lead
Groups linked to North Korea and Iran accounted for roughly two-thirds of newly observed dead-drop activity each quarter by the second quarter of 2026, according to the report. State-linked operators now represent around half of all activity Chainalysis tracks, up from a negligible share in early 2024.
Techniques differ by actor. A North Korean-linked operation associated with UNC5342 uses TRON and Aptos as alternate routes, while other campaigns rely on BNB Chain, Polygon and Bitcoin. Independent on-chain analysis by Bitquery found that one North Korean wallet named by Google in October 2025 has continued posting payloads, 251 in total, with the most recent on 8 September 2026. Bitquery estimates the whole setup cost around $85 in gas fees.
Why this matters
The danger is not greater destructive power. It is durability. Conventional attack infrastructure depends on servers and domains that hosting providers and law enforcement can seize or block. A public ledger cannot be switched off by any central authority, so instructions written to it remain reachable. Attackers can change their C2 servers simply by writing a new record, without reinfecting a single victim.
Blocking the traffic is also difficult. Blockchain RPC endpoints serve legitimate cryptocurrency services worldwide, so defenders cannot simply cut them off without collateral disruption. Chainalysis and others suggest that detection will increasingly depend on monitoring wallets, contracts and RPC traffic from corporate networks.
The Firevault view
Blockchain dead drops are a reminder that takedown is not a strategy. If attacker infrastructure can survive every seizure, the only reliable control is to remove the path between the malware and the data it is sent to find.
Malware can only retrieve instructions and exfiltrate records from systems it can reach. Data held on Offline Secure Storage® is physically disconnected when not in use, so there is no network path for a dead-drop command to exploit, however permanent the ledger that carries it. Organisations should ask a simple question: which of our critical records would still be reachable if an implant on our network received new orders tomorrow?
Sources
- Chainalysis, "DPRK and Iran are Leading a 5.2x Surge YoY in Blockchain-Assisted Cyberattacks", 17 September 2026
- Bitquery, "EtherHiding and Blockchain Malware, Measured On-Chain", 18 September 2026
- Cyber Security Intelligence, "Hackers Fuel Blockchain Dead Drops", 21 September 2026
- TechRadar Pro and Insurance Journal reporting, September 2026
Questions
It is a technique where attackers store malware instructions or command server addresses inside public blockchain transactions or smart contracts. Infected devices read those records to receive new orders, and because the ledger cannot be deleted, the channel survives server takedowns.
Chainalysis reports a 440% year-on-year rise, with malicious blockchain writes increasing from 2.06 to 11.1 a day in less than a year.
Groups linked to North Korea and Iran accounted for roughly two-thirds of newly observed activity each quarter by the second quarter of 2026, according to Chainalysis.
Monitor for unexpected blockchain RPC traffic, and keep the most critical records physically disconnected when not in use, so that malware has no network path to them regardless of where it receives its instructions.
Sources and reporting notes
- cybersecurityintelligence.comPrimary reporting referenced in this analysis.
Incident facts are attributed to the named sources; the recommendations and product discussion are Firevault analysis by Mark Fermor.
About the author
Mark FermorCTO, CMO and Founder of Firevault. Mark writes on physical control, offline storage and the incidents that show why both matter.
Why #OSS
Keep a clean copy out of reach.
Offline Secure Storage® keeps one copy physically disconnected at the hardware level between sessions.
Control
Govern the paths attackers depend on.
Physical, out-of-band control of selected network paths, composed into Control Plans and industry Blueprints.
Ready to start?
Create your Vault online.
Business Vaults from £360 a month inc VAT, on a 36-month commitment.