300GB fixed
LUV
One nominated day each week, within a 12-hour window
Closed matters and preserved records that are rarely reopened
Explore LUVOffline Secure Storage® gives legal practices a physically disconnected home for client files, matter records and critical firm data, aligned with the preservation principles legal-sector guidance now expects.
The Canadian Bar Association brings together professional duties around confidentiality, integrity, availability, retention and recovery. Its guidance is international good practice rather than UK regulation, and it maps closely to what SRA, ICO and NCSC sources expect of UK firms.
Records must be protected from alteration, corruption and destruction, with recoverable copies of important files maintained.
Files must remain readable and usable over the long term, not merely exist somewhere in storage.
A written backup and disaster-recovery plan is part of competent data and file management.
Multiple backups, staggered at different points in time, rather than reliance on one current copy.
The existence of a backup is not enough. Firms should routinely verify that data can actually be restored.
Connected backups face the same risks as production systems. Guidance recommends moving a full backup off-network, described as air gapped, to a secure location.
Backups should be fully encrypted, at rest and in transit.
Recovery copies must be protected to the same standard as the original information, or the recovery architecture itself becomes a confidentiality risk.
Firms should set a recovery time objective and recovery point objective that reflect obligations to clients and the regulator.
Due diligence on providers, clarity on where data is stored, and a preference for services where the firm can hold its own encryption keys.
Keep information for the period professional and statutory obligations require, then destroy it securely. Clicking delete is not sufficient for confidential data.
A documented approach covering what is backed up, how frequently, who is responsible and which records are recovered first.
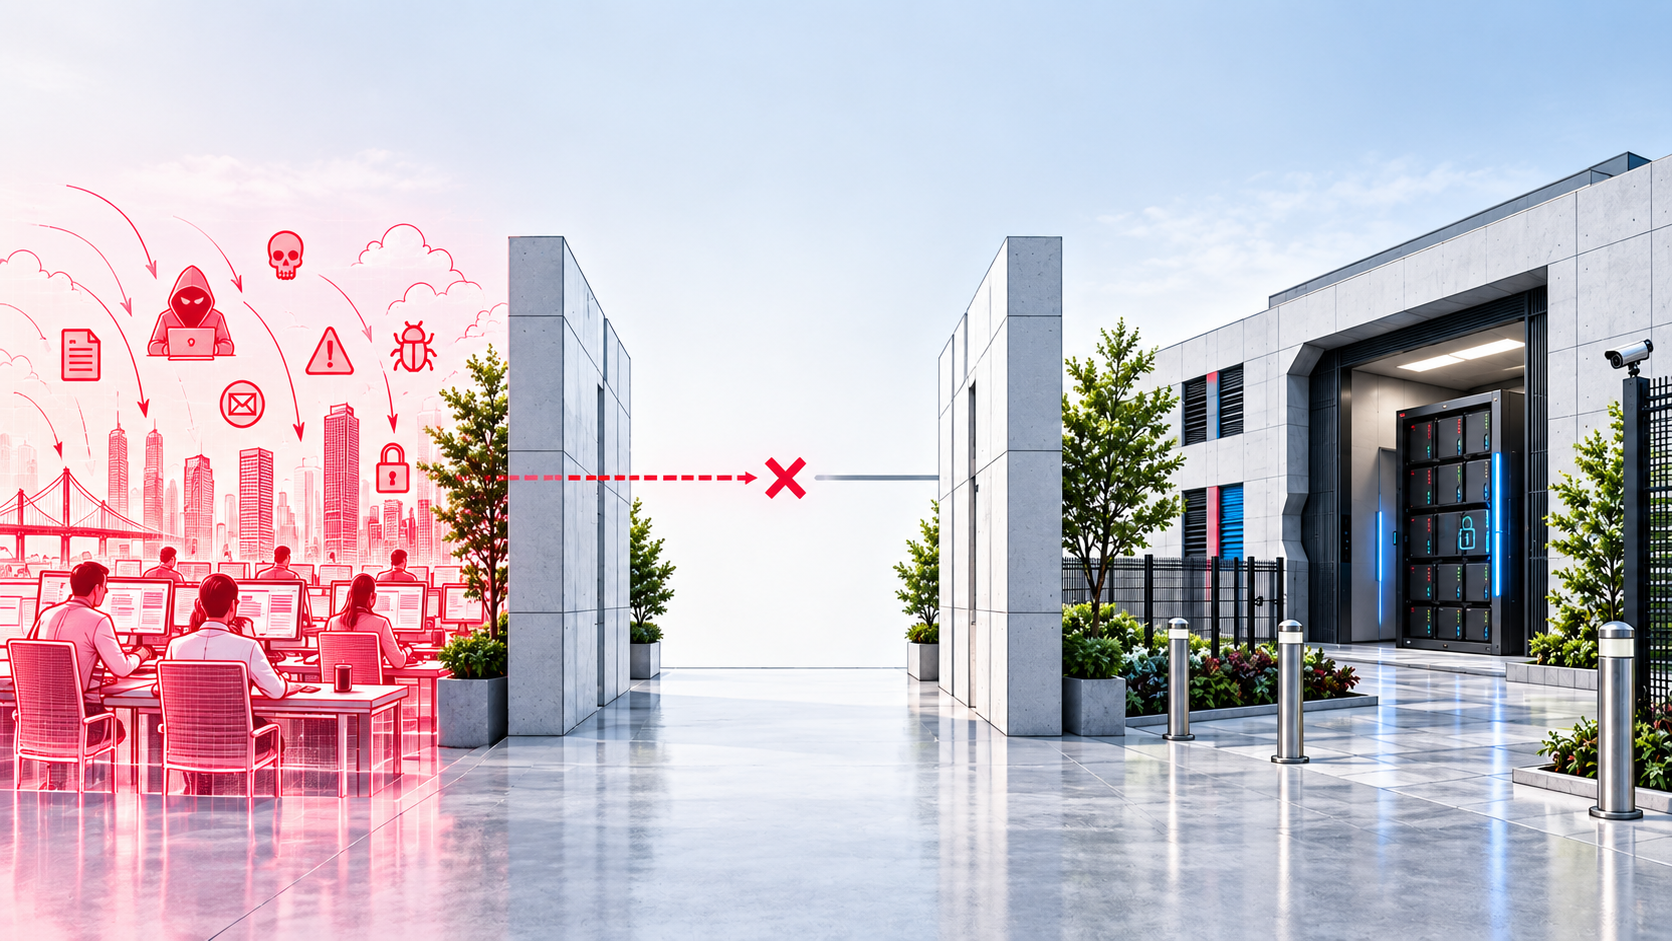
CBA guidance states that full backups should be separated from the rest of the network, because connected backups face the same risks as production systems. That is precisely what Firevault is.
Guidance principle
Separate full backups from the network
Firevault answer
Physically disconnected hardware with no standing network path.
Guidance principle
Secure off-site copies
Firevault answer
Dedicated storage held in a separate secure environment.
Guidance principle
Integrity and recoverability
Firevault answer
Dedicated physical storage, controlled access and offline audit records.
Guidance principle
Confidentiality and control over third parties
Firevault answer
One Vault to One User, controlled access and customer-held key options.
Guidance principle
Withstand ransomware and disruption
Firevault answer
The protected copy is unreachable while physically disconnected.
Recovery objectives are set by the firm's plan. The storage simply has to honour them without staying exposed.
300GB fixed
One nominated day each week, within a 12-hour window
Closed matters and preserved records that are rarely reopened
Explore LUV2TB, 4TB or 8TB
24/7 on-demand access
Active preservation copies and records the firm may need quickly
Explore VaultFrom 20TB
Designed around organisational requirements
Firm-wide preservation above 8TB and multi-office programmes
Explore StorageCBA guidance is persuasive international practice. The obligations that bind UK firms come from the SRA, UK GDPR and NCSC. Firevault supports the controls; the firm and its advisers own compliance.
The Canadian Bar Association's guidance on digital record preservation, backup and business continuity, including air-gapped full backups and tested restoration.
Read the official sourceParagraph 6.3 requires the affairs of current and former clients to remain confidential unless disclosure is required or permitted by law or the client consents.
Read the official sourceClosed files should be stored securely to protect confidentiality and archived or destroyed promptly where appropriate.
Read the official sourceICO guidance says personal data must not be kept longer than needed, with documented retention periods and periodic review.
Read the official sourceNCSC recommends keeping important backups separate from the network so ransomware cannot reach them.
Read the official sourceStraight answers on how Offline Secure Storage® behaves in practice.