
News
Fake job interviews infected 30,000 devices, FBI-led advisory says
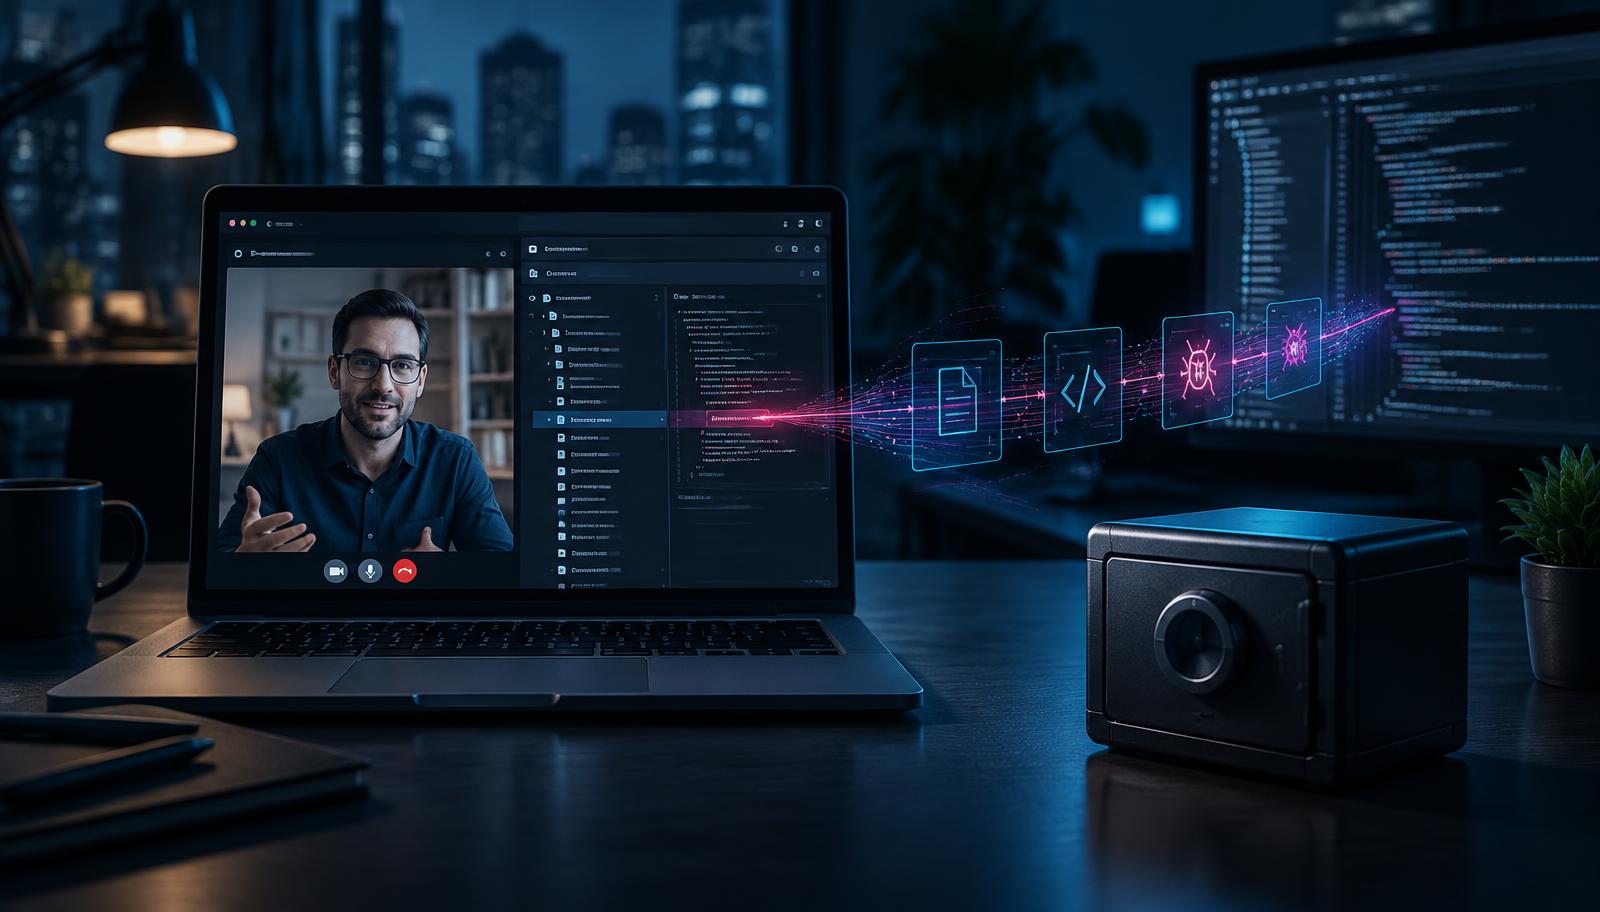
A joint FBI-led advisory says North Korean WaterPlum actors used fake technical interviews and coding tests to infect at least 30,000 devices in more than 100 countries.
Mark FermorCTO, CMO and Founder, Firevault
Published 25 September 2026 · 5 min read
What the agencies reported
A joint advisory published on 18 September by cyber and intelligence agencies in Japan, the United States, Australia and Germany says a North Korean-linked campaign has infected at least 30,000 devices in more than 100 countries.
The agencies call the group WaterPlum. Security researchers more commonly track the activity as Contagious Interview. According to the advisory, the actors pose as recruiters or prospective employers, often impersonating legitimate artificial intelligence, cryptocurrency and NFT businesses. They approach software developers and other IT professionals through social media, job sites, gig-work platforms and freelance marketplaces.
The figures are official assessments rather than independently audited totals. The advisory says the campaign has stolen funds or account credentials from more than 7,000 cryptocurrency wallets and transferred ¥1.7 billion, approximately US$10.71 million, in cryptocurrency assets to North Korea.
The interview is the delivery mechanism
The initial approach is designed to look like ordinary recruitment. During a video interview or coding assessment, the candidate is asked to download a project, repair a supposed conferencing fault or run code from a developer platform or repository.
The advisory names malicious npm packages, GitHub or Bitbucket repositories and Visual Studio Code projects as delivery routes. Malware families linked to the activity include BeaverTail, InvisibleFerret, OtterCookie, OtterCandy and StoatWaffle.
Once executed, the malware can create persistent remote access, steal browser credentials and cryptocurrency information, capture clipboard or keystroke data, take screenshots and collect identity documents. A compromised developer machine can also become a route into the organisation that employs that person.
That wider risk matters. This is not only a cryptocurrency theft campaign. The advisory warns that successful infections can create opportunities for espionage, intellectual property theft and lateral movement through corporate systems.
The laptop-farm connection
The same advisory connects WaterPlum infrastructure with North Korean IT workers who obtain legitimate-looking remote contracts using false or borrowed identities.
A laptop farm is a collection of employer-issued computers physically hosted by an enabler and remotely operated from another country. Japan says it identified and dismantled its first domestic laptop farm. The FBI says it continues to identify and prosecute US-based facilitators.
The Japanese National Police Agency and FBI assess that WaterPlum actors and some North Korean IT workers operate under the 313 General Bureau of North Korea's Munitions Industry Department. That wording is an intelligence assessment, not a judicial finding.
What developers and employers should do
Developers should not run unfamiliar interview code on the same machine that holds employer access, personal data or cryptocurrency credentials. Unknown projects should be inspected before execution and, where testing is necessary, opened only in an isolated sandbox or virtual machine.
The advisory highlights suspicious commands and obfuscated scripts, including use of curl, base64, mshta, Invoke-WebRequest and hidden execution. A command containing one of these terms is not automatically malicious, but a recruiter who asks a candidate to run code they cannot explain should be treated as a serious warning sign.
Employers should verify remote applicants beyond identity documents and a short video call. The agencies recommend checking whether the applicant's network location broadly matches their claimed residence, testing detailed knowledge behind unusually broad CV claims, verifying qualifications and investigating payment requests involving cryptocurrency or accounts in another person's name.
Access must remain limited to what a contractor needs. If an identity or subcontracting concern emerges, revoke accounts and active sessions promptly rather than waiting for the investigation to finish.
If a machine may be infected
The advisory says to disconnect the affected device from the internet immediately. Removal of the detected malware is not enough, because information may already have been stolen and other persistence may remain.
Cryptocurrency assets should be moved to a new wallet created on a separate clean device, with the new seed phrase stored offline. Essential data should be recovered carefully before a full operating-system reset, and organisations should use endpoint monitoring to look for related behaviour elsewhere.
The Firevault view
The most important lesson is the trust boundary. A coding task can turn a developer's everyday workstation into an attacker-controlled foothold, and that workstation often holds access to source code, credentials, shared drives and recovery systems.
Detection and recruitment checks reduce the likelihood of compromise, but they do not answer the recovery question: what remains trustworthy after the machine and its connected identity have been exposed?
Critical recovery data held in Offline Secure Storage® is physically disconnected when it is not being used. Malware on a developer endpoint cannot browse, encrypt or exfiltrate a copy for which no network path exists. Organisations should keep the recovery copy outside the reach of developer tools, cloud identities and remote administration, then test that it can be restored without trusting the compromised estate.
Sources
- Joint FBI, NPA, NCO, DC3, ACSC, BND and BfV advisory: WaterPlum and Contagious Interview, 18 September 2026
- Australian Cyber Security Centre publication of the joint advisory
- Palo Alto Networks Unit 42: Contagious Interview and Wagemole, 21 November 2023
- Zscaler ThreatLabz: technical analysis of North Korean remote-worker activity
Questions
WaterPlum is the name used in a joint 2026 government advisory for a North Korean-linked cyber group more widely tracked by researchers as Contagious Interview. It targets developers and IT professionals with fake recruitment approaches and malicious coding tasks.
The actor poses as a recruiter or employer and asks the candidate to download a project, complete a coding test or troubleshoot a supposed video-call problem. The supplied package or repository runs malware that can steal credentials, cryptocurrency information and other sensitive data.
The joint advisory says at least 30,000 devices in more than 100 countries were infected and more than 7,000 cryptocurrency wallets had funds or credentials taken. These figures are official agency assessments and have not been independently audited.
Disconnect the device from the internet, inform the employer or security team, assume credentials and sensitive data may have been exposed, rotate them from a separate clean device and investigate before rebuilding the operating system. Cryptocurrency should be moved to a new wallet created on another clean device.
Sources and reporting notes
- ic3.govPrimary reporting referenced in this analysis.
Incident facts are attributed to the named sources; the recommendations and product discussion are Firevault analysis by Mark Fermor.
About the author
Mark FermorCTO, CMO and Founder of Firevault. Mark writes on physical control, offline storage and the incidents that show why both matter.
Why #OSS
Keep a clean copy out of reach.
Offline Secure Storage® keeps one copy physically disconnected at the hardware level between sessions.
Control
Govern the paths attackers depend on.
Physical, out-of-band control of selected network paths, composed into Control Plans and industry Blueprints.
Ready to start?
Create your Vault online.
Business Vaults from £360 a month inc VAT, on a 36-month commitment.