Revolut handed customer data to criminals for five months. Then came a $3 million ransom demand
Revolut handed sensitive customer data to criminals impersonating an Italian government agency for five months. Now a three million dollar ransom demand has gone public. Mark Fermor argues the real question is not how it happened, but why the process allowed it.
Why it matters
What this means for organisations holding critical data
Revolut handed sensitive customer data to criminals impersonating an Italian government agency for five months. Now a three million dollar ransom demand has gone public. Mark Fermor argues the real question is not how it happened, but why the process allowed it.
What happened
Revolut has confirmed that sensitive customer data was disclosed to an unauthorised third party after fraudulent requests for information were submitted from an email account within a legitimate government agency domain. The request looked genuine, because part of it was.
Update, 18 September 2026. Since this piece was first published, the picture has become considerably worse. Reporting by SecurityWeek, the Financial Times and others now indicates that Revolut was responding to the fraudulent requests for roughly five months before the fraud was detected. Around 680 customers, believed to include high profile account holders, are affected. The impersonated agency is reported to be an Italian prefecture in Reggio Calabria, whose compromised institutional email account was used to pose as law enforcement.
On Wednesday, a threat actor using the name IAmNotAVillain publicly demanded a ransom of three million dollars, payable in the privacy coin Monero, threatening to sell the customer data to other criminal groups if payment is not made. Making an extortion demand public from the outset is unusual, and Revolut says it has received no direct contact or demand from the individuals behind the claims. Italian prosecutors and the National Anti Mafia and Counter Terrorism Directorate have opened an investigation.
According to the customer notification reviewed by TechCrunch, the compromised information included dates of birth, postal and email addresses and phone numbers, as well as copies of identity documents such as passports and driving licences. Verification selfies, account statements and transaction histories, including cryptocurrency transactions, may also have been exposed.
Revolut says the affected customers have been contacted directly. The company blocked the email address used in the fraud after detecting the incident, alerted the agency, law enforcement, data protection authorities and financial regulators, and says its systems and customer funds were unaffected. The incident was first highlighted publicly by crypto security researcher ZachXBT, who suggested the breach appeared to have targeted high net worth users.
We are asking the wrong question
Everyone wants to know how it happened. I am far more interested in why the process allowed it to happen, and allowed it to keep happening for five months.
Nobody hacked their way in. Nobody bypassed some cutting edge security control. A request arrived, it looked legitimate enough, and sensitive customer information was handed over. Then another request arrived, and another, month after month. That should make every organisation stop and think.
We spend huge amounts of time and money testing technology. We run penetration tests. We monitor alerts. We patch vulnerabilities. We invest in new tools. But how many organisations test the decisions their people make when a request appears to come from an authority they trust? And how many review patterns of requests over time, so that a slow drip of disclosure is spotted before it becomes five months of it?
This is where many businesses get caught out.
Compliant and vulnerable at the same time
Two things can be true at once. You can be compliant, and you can still be vulnerable.
The problem is that many organisations behave as though those two things cannot possibly coexist. I have seen businesses with immaculate policies, successful audits and folders full of evidence. Yet when you start looking at their processes through an attacker's eyes, cracks begin to appear.
Not because they are careless. Not because they are incompetent. Because nobody has ever challenged the process in the real world.
That is the difference between documenting a process and proving it works. The organisations that worry me are not the ones that know they have gaps. It is the ones that are convinced they do not.
The question worth asking
If someone targeted your organisation tomorrow with a legitimate looking request for customer, employee or financial data, are you confident your process would stop them? Or are you confident your process is documented?
They are not the same thing.
This is also where the data itself matters. Revolut disclosed copies of passports, driving licences and possibly statements and transaction histories because that material was retained and reachable through a routine request process. Where identity records and historical documents must be kept, Offline Secure Storage® keeps them physically disconnected from the systems and inboxes that field incoming requests, so disclosure becomes a deliberate, verified act rather than a response to a convincing email.
Test the process, not just the perimeter. And do not leave your most sensitive records permanently reachable by whoever asks nicely enough.
Mark Fermor is the founder of Firevault.
Sources
- SecurityWeek: Revolut data breach, five months, 680 high profile accounts, three million dollar ransom
- Euronews: Revolut hack, criminals steal data of 700 European clients, demand three million dollar ransom
- OCCRP: Hackers demand three million dollar ransom in Revolut data leak
- FStech: Revolut confirms customer data breach after fake government requests
- Mark Fermor on LinkedIn
How Firevault would handle this
Controls an auditor can physically verify
Firevault gives you physical separation, named custody and evidenced access, so compliance claims about isolation and control are things you can show, not just assert.
Related Reading
You may also find these useful
When data theft becomes personal: what we discussed at The Chelmsford Club
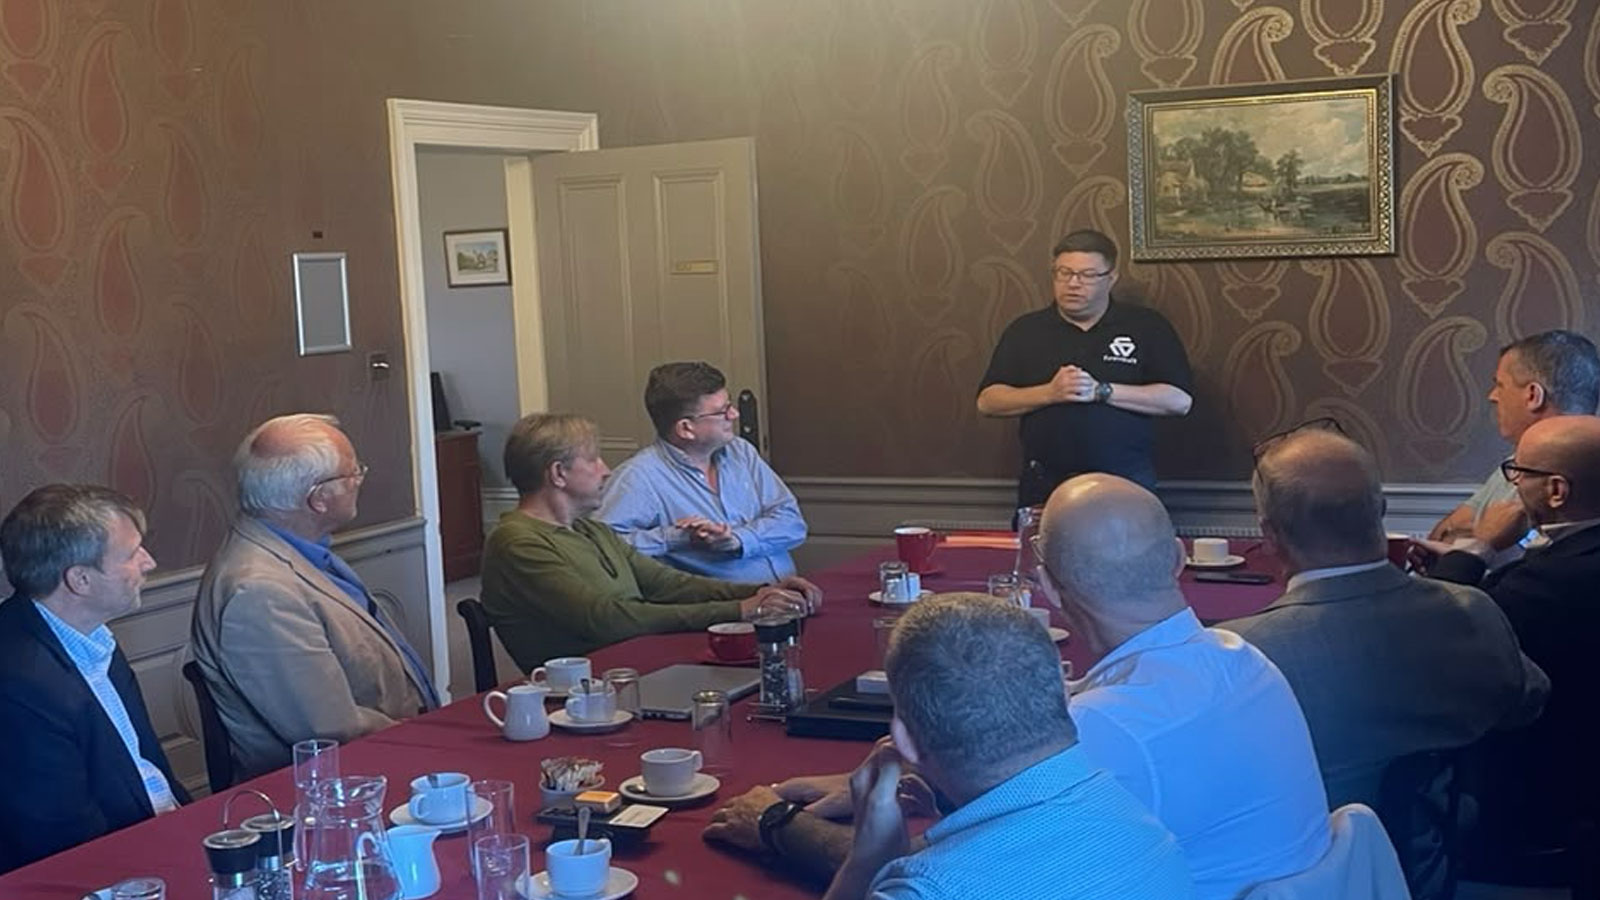
Mark Fermor joined the Inner Circle breakfast at The Chelmsford Club to talk about cyber attacks, data theft and what happens when information a business has been trusted to hold ends up in somebody else's hands. The real value of stolen data is not what somebody will pay for it. It is what that information allows them to do next, and the consequence lands personally, professionally and commercially.
Nissan / PeopleSoft Breach: When HR Is Also Your Financial Data Repository
Nissan Americas has confirmed employee SSNs, banking and tax data were exposed through the Oracle PeopleSoft zero-day (CVE-2026-35273) campaign linked to ShinyHunters. Mark Fermor on why HR systems keep becoming citizen-scale breaches.
Tata / Apple Leak Shows Why Supply-Chain Data Belongs Off the Wire
World Leaks has posted iPhone 18 Pro supplier maps and drop-test photos taken from Apple's Indian manufacturer Tata Electronics. Mark Fermor on why the answer is architectural, not contractual.
Conwy Council Breaches Show the Insider Threat Regulators Keep Underestimating
Three separate disciplinary outcomes in one department in twelve months. Mark Fermor on why the Conwy County Council data breaches are a structural warning to every UK local authority, not a one-off.
FortiBleed Proves the IP-Connected Perimeter is Indefensible
SOCRadar has now tied the FortiBleed credential-harvesting operation directly to INC and Lynx ransomware deployments. Mark Fermor on why physical severance is the only durable answer.
Dyfed-Powys Police confirms cyber attack as staff information may have been compromised
Dyfed-Powys Police has confirmed that a cyber attack identified on 14 September disrupted non-emergency systems and may have exposed staff information. The force says it has found no evidence that public data was accessed.