
Opinion · Commentary · Breaking
The PRA is right to warn the City. But resilience needs more than supervision.
The new head of the Prudential Regulation Authority has told banks and insurers to get serious on cyber resilience, days after a cloud failure disrupted Lloyds, HSBC and Revolut. Mark Fermor argues that supervision alone cannot remove the standing connections attackers and outages exploit.
Mark FermorCTO, CMO and Founder, Firevault
Published 24 October 2026 · 4 min read
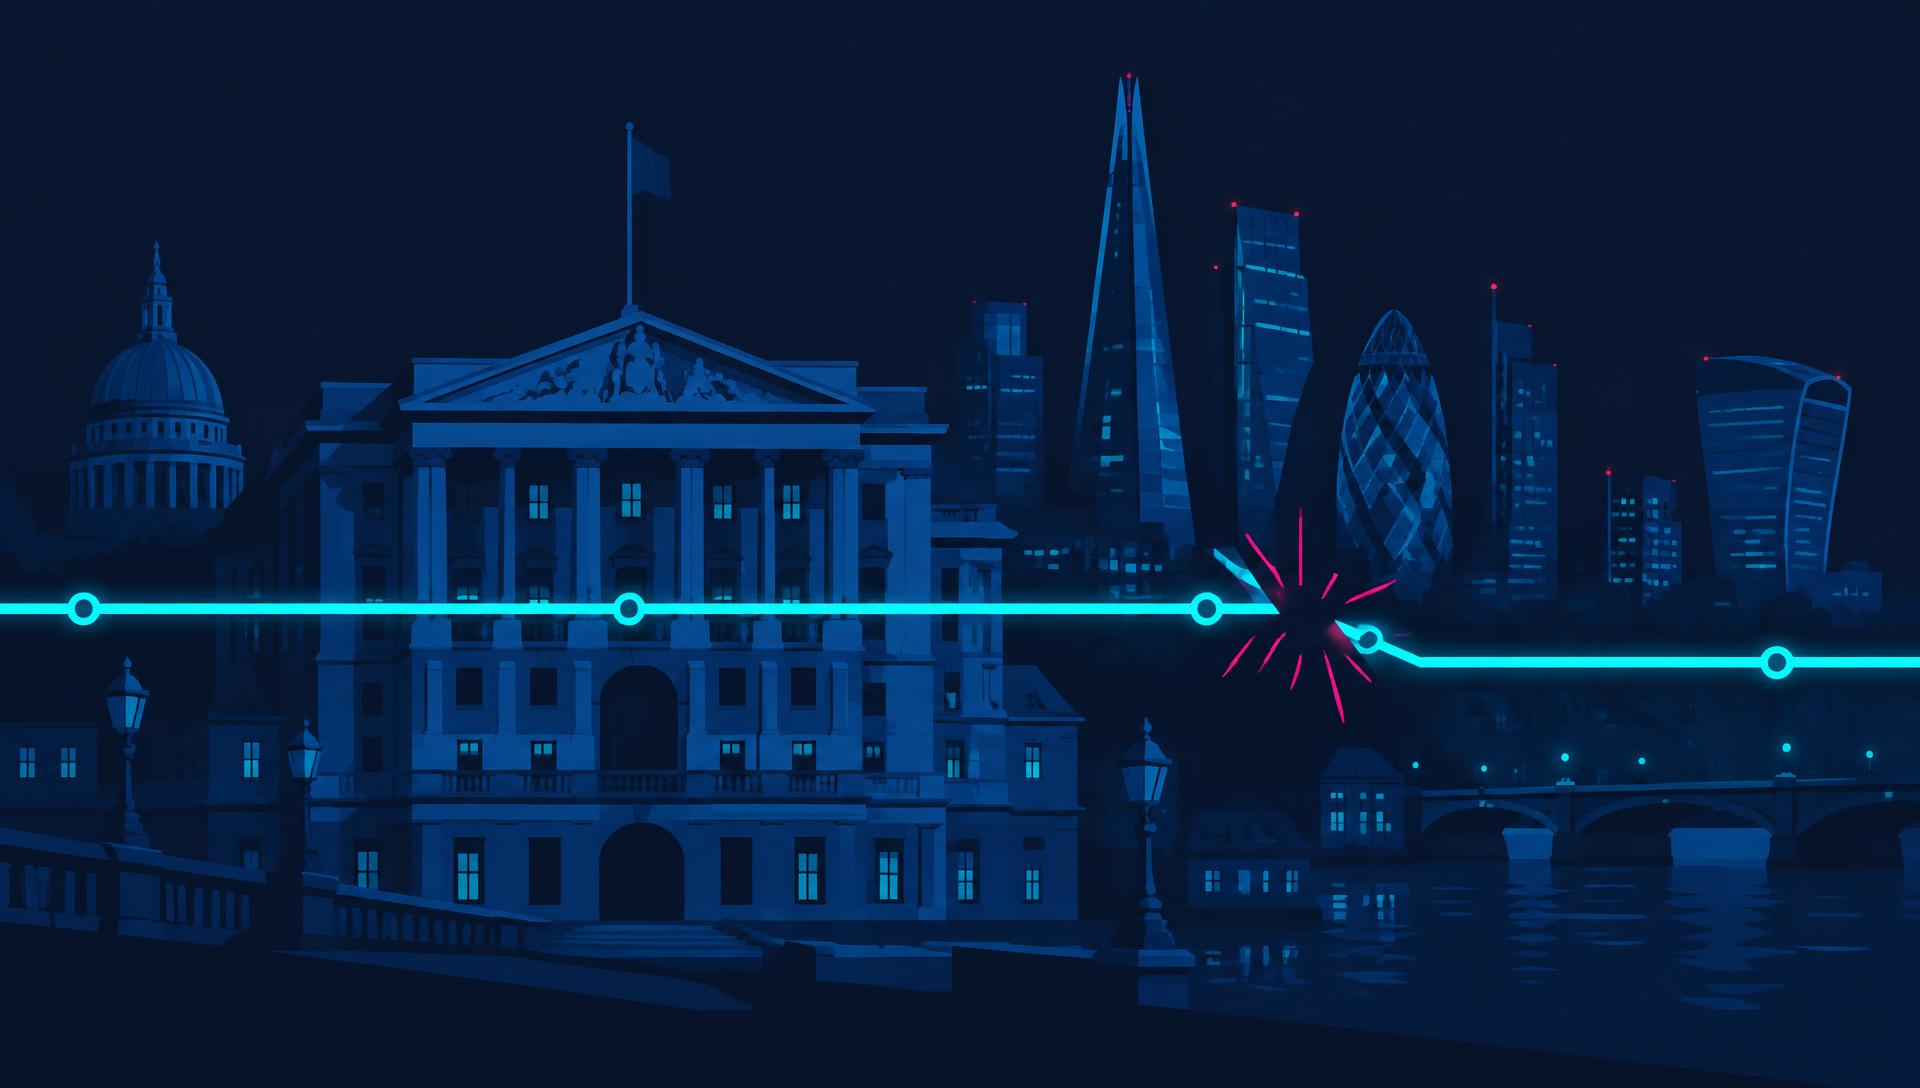
Illustration of the City of London skyline with a glowing network connection being physically severed
What happened
The City of London's newest senior regulator has put banks and insurers on notice over their cyber defences. In her first speech since taking charge of the Bank of England's Prudential Regulation Authority in July, Katharine Braddick told an audience at Mansion House on Thursday 22 October 2026 that the PRA would "significantly increase" its focus on firms' operational and cyber resilience, according to The Times.
Braddick is creating a dedicated directorate within the regulator to concentrate on this area, reporting directly to her. The PRA and the Financial Conduct Authority will consult on emerging risks before the end of the year to clarify what they expect of firms.
The timing was pointed. Two days earlier, a failure in Google Cloud's London operations disrupted the websites and apps of Lloyds, HSBC and Revolut. Revolut was hit hardest: card payments, transfers and cash machine withdrawals were all affected. Nikhil Rathi, the FCA's chief executive, cited the incident in his own Mansion House speech, warning that "the threats to market integrity are as serious as I have seen them".
A welcome warning. A familiar answer.
This is the right warning at the right time, and a new directorate with a direct line to the chief executive signals genuine intent. The City should take it seriously.
But notice what the proposed answer looks like: more supervision, more expectations, more consultation. These are necessary. They are also variations on the same model the industry has followed for two decades, in which resilience means defending connected systems more vigorously and recovering from failure more quickly.
The Google Cloud incident showed the limits of that model in a single afternoon. One provider's failure reached three major banks at once, not because any of them were hacked, but because they were all connected to the same dependency. Concentration risk is connection risk. When everything is connected to everything, a fault anywhere can become a problem everywhere.
The question supervision cannot answer
Regulators can raise standards, demand evidence and test recovery plans. What no framework can do is change the physics of a connected system. If data is connected, it can be reached, whether by an attacker, a faulty update or a failing supplier.
So alongside every resilience plan, boards should be asking a harder question:
Which of our systems and data should never be continuously reachable in the first place?
Settlement records. Customer archives. Recovery copies. The crown jewels that an institution cannot afford to lose or have altered. Keeping these continuously online is a choice, not a law of nature, and it is a choice that deserves scrutiny at board level.
What genuine resilience looks like
At Firevault we argue that resilience has two halves. The first is defending the connected estate, and the regulators are right to demand more of it. The second is deciding what does not need to be connected at all.
Offline Secure Storage® holds an organisation's most valuable data on dedicated hardware that is physically disconnected and offline by default. Authorised access is established when required and removed when the session ends. Control by Firevault applies the same principle to operational connections, so a path into a critical system exists when approved work needs it and physically does not when it does not.
Neither removes the need for supervision, detection or response. Both remove a standing path that an incident, criminal or accidental, could otherwise travel.
The PRA is asking the City to get serious. The most serious question a board can ask is not how well it defends its connections, but which connections should exist at all.
Mark Fermor is CTO, CMO and Founder of Firevault. Learn why offline storage is different or talk to the team.
About the author
Mark FermorCTO, CMO and Founder of Firevault. Mark writes on physical control, offline storage and the incidents that show why both matter.
Why #OSS
Keep a clean copy out of reach.
Offline Secure Storage® keeps one copy physically disconnected at the hardware level between sessions.
Control
Govern the paths attackers depend on.
Physical, out-of-band control of selected network paths, composed into ten Blueprints.
Ready to start?
Create your Vault online.
Business Vaults from £360 a month inc VAT, on a 36-month commitment.