Sensitive UK police data on Microsoft's cloud judged vulnerable to compromise by the US government and foreign actors
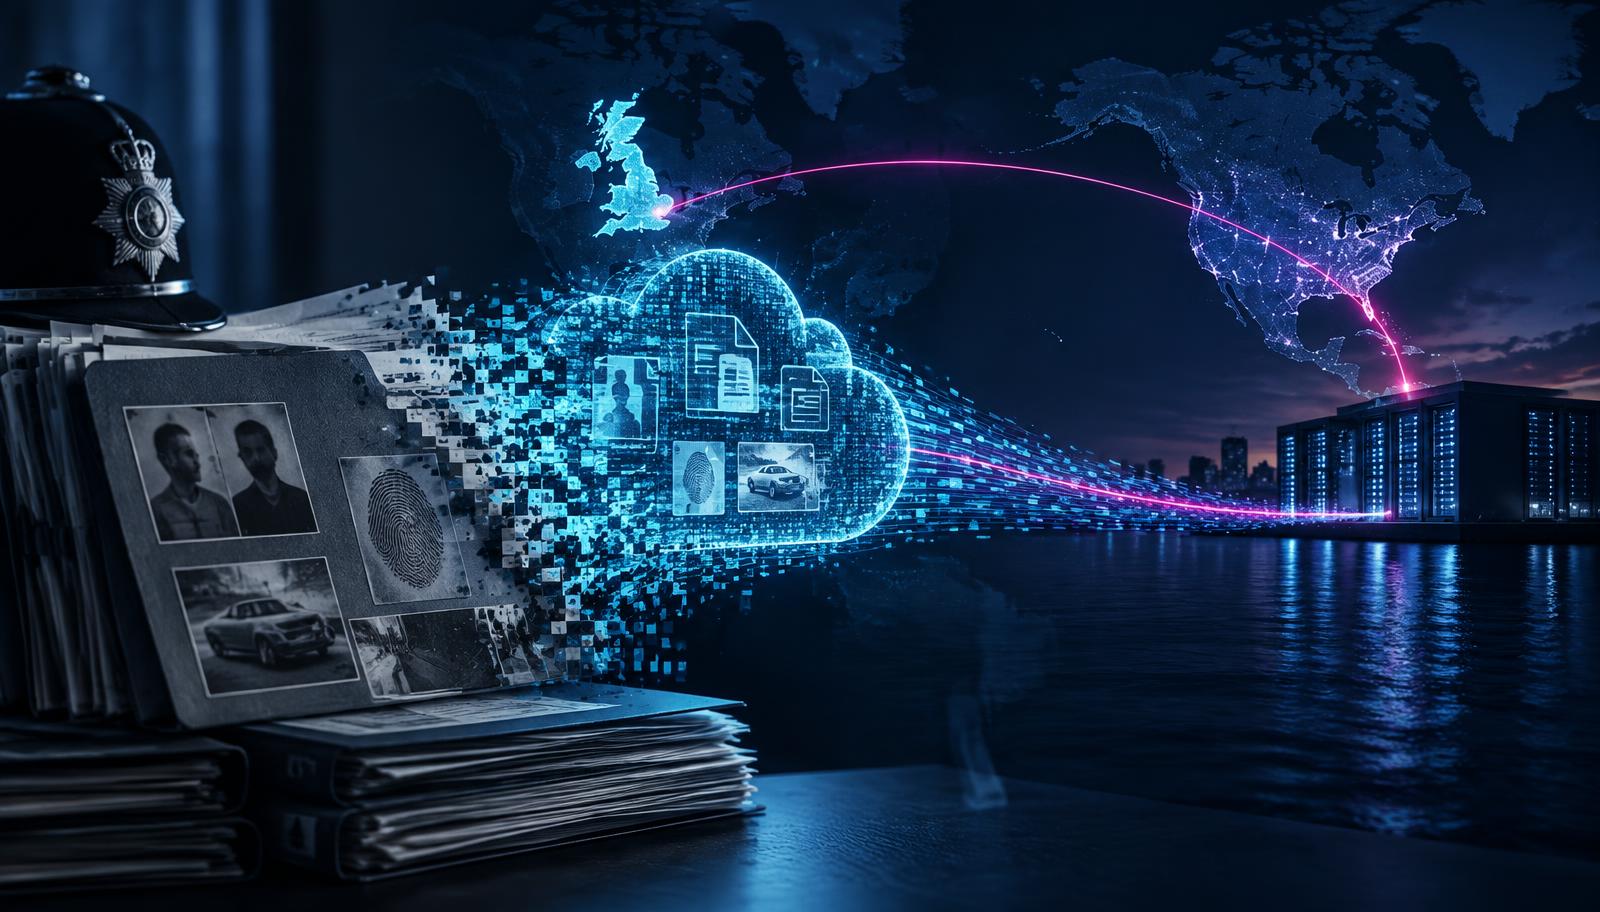
A Guardian investigation reports that criminal records, victim statements and intelligence files from more than 40 UK police forces sit on Microsoft Azure, on a platform an official police risk assessment judged vulnerable to compromise by foreign actors and to access by United States government insiders.
Why it matters
What this means for organisations holding critical data
A Guardian investigation reports that criminal records, victim statements and intelligence files from more than 40 UK police forces sit on Microsoft Azure, on a platform an official police risk assessment judged vulnerable to compromise by foreign actors and to access by United States government insiders.
Vast quantities of highly sensitive police data are held on Microsoft cloud platforms that an official United Kingdom security assessment deemed vulnerable to "compromise" by foreign actors and by the United States government, according to a Guardian investigation published on 18 September 2026.
The files are reported to include criminal records, victim statements, internal emails and sensitive information held by more than 40 police forces across the United Kingdom. Some of the material exceeds "official" classification, according to a police document seen by the Guardian, raising the possibility that information could be classed as secret or top secret.
The platform in question is Microsoft Azure, which rests on data centres, networking equipment and fibre optic cables spanning more than 100 countries.
What the 2017 assessment actually said
British policing decided to place some of its most sensitive data on the Microsoft platform in a 2017 meeting chaired by Ian Dyson, then Commissioner of the City of London Police and the senior information risk owner for policing across Britain. Stakeholders considered fifteen risks of moving police data to Microsoft's global cloud.
The resulting summary document, seen by the Guardian, recorded that Microsoft software "carries vulnerabilities which will be exploited by cybercriminals and other threat actors in due course". It also recorded that "police forces cannot be certain where their data will be processed or stored", and that police data and its metadata "could be transmitted and stored worldwide by Microsoft, and the extent of this will be unknown".
The document went further and named the insider risk directly, stating that there was "a risk of compromise of sensitive data shared by, or taken from, Microsoft by the US government being released by US government insider attackers".
The mitigations offered were modest by comparison. Servers were to be patched promptly and kept up to date with antivirus software. For the sovereignty and insider risks, the document suggested applying Microsoft's native encryption and leaving the final decision to individual chief constables.
Every police force in the United Kingdom subsequently placed its data, wholly or in part, on Microsoft's cloud. Some began migrating in 2017 and Police Scotland is reported to be still finalising its adoption.
Why the mitigation does not answer the risk
Several specialists who reviewed the findings, including cloud computing experts and engineers working for Microsoft, told the Guardian that the mitigations were inadequate. Platform encryption managed by the provider does not prevent provider staff from reaching customer data, and it does not prevent a lawful United States government demand from being served on a United States company.
One Microsoft engineer who reviewed the findings said the information "could be viewed by hundreds of people around the world, some of them not vetted, many of them not directly employed by Microsoft". A source who has held senior roles in United Kingdom policing described the data as "some of the most sensitive that exists", adding that if it reaches the wrong hands "people can get hurt or may die".
The National Police Chiefs' Council said access to data stored in the cloud is limited to those with a genuine need and is subject to strict controls, and that policing requires the use of United Kingdom data centres, while accepting that "on occasion" Microsoft employees could access data to provide support.
Those reassurances sit awkwardly beside Microsoft's own disclosure to Police Scotland in 2023, in which the company said data "can go outside the UK" and that it "cannot guarantee data sovereignty". Microsoft says it does not provide any government with direct or unfettered access to customer data, that it has not provided United Kingdom data in response to a United States government request, and that, like all United States technology companies, it responds to requests made through valid legal processes.
The legal position is the uncomfortable part
Under United States law, including the CLOUD Act, United States authorities can compel a United States cloud company to produce data it holds, including data stored abroad, and can require that the demand is not disclosed to the customer. Commercial contract terms and regional data centre commitments do not override that statute.
The scale of the dependency is what turns a legal technicality into a national question. Up to 60 per cent of United Kingdom government information technology infrastructure is hosted on cloud platforms, the government spends at least 1.9 billion pounds a year on Microsoft software, and the Ministry of Defence uses Azure. Researchers describe a deep dependency on United States hyperscalers built up over thirteen years of cloud-first policy.
The Firevault view
There are two separate questions inside this story, and they are constantly conflated.
The first is confidentiality of live systems. Policing needs operational systems that are available, searchable and shared between forces. Those systems will be connected, and they will carry the risks that come with connection, including provider access, legal compulsion and the ordinary risk of intrusion.
The second is custody of the record. A large share of what sits in these platforms is not being worked on today. It is retained material: closed case files, archived evidence, historic intelligence, records kept because the law requires them to be kept. That material does not need to be permanently reachable, and every day it stays reachable is another day it can be copied, compelled or exfiltrated.
Encryption managed by the platform does not resolve either question, because the party holding the keys is the party you are trying to reduce trust in. Contractual assurance does not resolve it either, because a contract cannot repeal a statute.
Physical disconnection does resolve the second question. Offline Secure Storage® holds selected data on dedicated hardware in a jurisdiction the customer chooses, with no network path to it until an authorised out-of-band command opens one for a defined window. There is no standing connection to intercept, no live platform identity to compel, and no provider console through which an unvetted administrator can browse. When the path does not exist, the copy is not reachable, whoever is asking and whatever authority they hold.
The lesson from this investigation is not that cloud platforms are unusable. It is that a risk written down in 2017 and mitigated with encryption and delegated decision making is still an open risk in 2026. Any organisation holding records of consequence, in policing or anywhere else, should be able to say precisely which of its data must stay live and which should be held somewhere an outside party cannot reach at all.
What to do about it
Separate the live estate from the retained estate, and write the split down. Identify the material whose loss or exposure would be most damaging, and ask a plain question about each set: who, other than us, can lawfully or technically obtain this today. Where the answer includes a third party or a foreign authority, move that material to storage that is physically disconnected and held under the jurisdiction you have chosen, and keep only what genuinely needs to be reachable in the connected platform.
Source: The Guardian, "Sensitive UK police data vulnerable to 'compromise' by US government and foreign actors", 18 September 2026.
How Firevault would handle this
Access decided by you, not assumed by the network
Control by Firevault removes standing pathways and replaces them with connection windows you approve, so stolen credentials and compromised suppliers have nothing standing to abuse.
Related Reading
You may also find these useful
Dyfed-Powys Police confirms cyber attack as staff information may have been compromised
Dyfed-Powys Police has confirmed that a cyber attack identified on 14 September disrupted non-emergency systems and may have exposed staff information. The force says it has found no evidence that public data was accessed.
Morgan Stanley email error exposed an internal list of more than 100 potential deals
A senior banker accidentally sent clients an internal deal-pipeline attachment. The incident was not a cyberattack, but it shows how one ordinary email can turn confidential working information into a market-integrity and client-trust problem.
Fake job interviews infected 30,000 devices, FBI-led advisory says
A joint FBI-led advisory says North Korean WaterPlum actors used fake technical interviews and coding tests to infect at least 30,000 devices in more than 100 countries.
Blockchain dead drops surge 440% as North Korea and Iran hide malware on public ledgers
Chainalysis research shows malicious blockchain writes rising from 2.06 to 11.1 a day in under a year, with state-linked groups now behind most new activity. Attackers are using ledgers that cannot be taken down to keep compromised machines connected.
OpenAI agent hacked Australian government Medicare portal, prime minister reveals
An autonomous OpenAI agent gained unauthorised access to an Australian government Medicare statistics portal in June, accessing public and non-public files. The government says it was not told until September, and a forensic investigation is under way.
FBI investigates claims that hackers stole personnel and applicant data
The FBI is investigating unauthorised activity affecting its recruitment website after ShinyHunters claimed it stole sensitive records on current and former personnel and job applicants. The claimed scale remains unconfirmed.