Guides · 9 chapters · 3 min read
A Guide to Controlling Third-Party Access with a Control Blueprint
How Control Blueprint CP-03 uses Control Modules to give third parties access without giving them a permanent doorway, what good looks like, and how a deployment is scoped.
Chapter 1About this guide
This guide is written for security, infrastructure and risk leaders who need to give third parties access without giving them a permanent doorway. It explains one Control Blueprint, CP-03, in plain terms: the failure it addresses, the Control Modules it uses, how those modules work together, and how a deployment is scoped.
Control by Firevault is a suite of nine purpose-built modules: a set of tools and techniques that give you physical control over the paths into and across your estate. A Control Blueprint is a proven combination of those modules assembled for a specific outcome. This guide covers one blueprint. The Control overview covers the nine modules and the full set of blueprints.
Chapter 2The problem this blueprint addresses
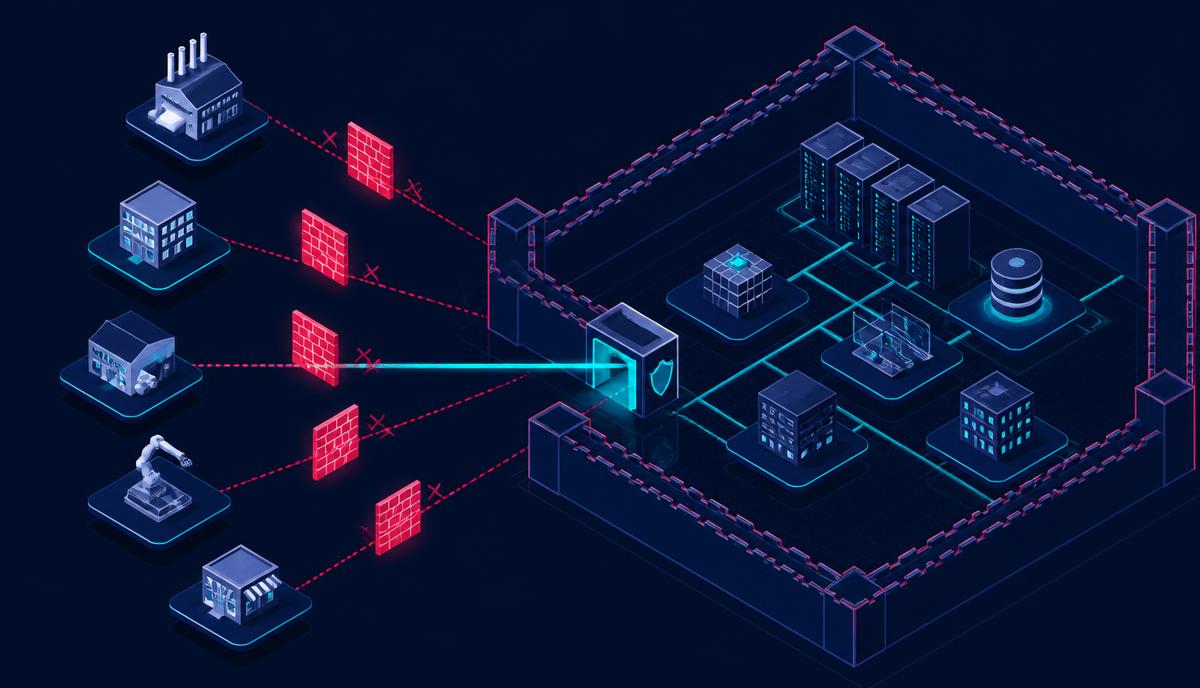
Most supplier access starts as a temporary arrangement and quietly becomes permanent. VPN tunnels, jump hosts and standing accounts remain long after the work finishes, and the organisation inherits the supplier security posture along with its own.
Chapter 3CP-03 at a glance
- Lead layer FIRE+VAULT
- Primary modules Validate, Relay, Lock
- Supporting modules Transfer, Archive, Execute
- Typical sectors Financial services, healthcare, energy and public sector
Chapter 4The primary modules
These modules do the work the blueprint is named for.
- Validate checks the request, command or identity before anything opens.
- Relay opens a controlled, time-bound crossing and closes it again on schedule.
- Lock holds access to the systems that matter behind identity and condition controls.
Chapter 5The supporting modules
These modules round out the pattern and are usually added as the deployment matures.
- Transfer governs what data is allowed to move, in which direction, and when.
- Archive preserves logs, records and evidence beyond the reach of the live estate.
- Execute fires the control action on signal, without waiting for a change window.
Chapter 6What good looks like
- No supplier path exists until a request is validated.
- Access windows close on schedule without human intervention.
- Only the approved role, system and function can be reached.
- Everything the supplier did is preserved for audit.
Chapter 7How the blueprint is deployed
Control Modules are a suite of tools and techniques deployed within your own estate and applied to the paths they govern: at a boundary, inside a zone, or at a third-party edge. Authorisation and evidence remain local, so losing connectivity to Firevault never opens a path.
Most deployments start with a single boundary or zone, prove the control behaviour, then extend the same blueprint across the estate. Modules can be customer-operated or co-managed.
Chapter 8How to scope it
Scoping starts with the paths, not the product. A short discovery exercise identifies the boundaries that matter, who needs to cross them, how often, and what evidence is required. That produces the module count and placement, which in turn produces the price. Blueprints are combined where an estate has more than one problem to solve.
Chapter 9Next steps
- Read the full blueprint detail: CP-03 blueprint
- See all nine modules and the other blueprints: Control by Firevault
- Talk it through with our team: contact Firevault
Where Firevault fits
Controls an auditor can physically verify
Firevault gives you physical separation, named custody and evidenced access, so compliance claims about isolation and control are things you can show, not just assert.
- 1Custody Named, access-controlled hardware in a Firevault Bunker
- 2Evidence Access windows and retrieval events are recorded
- 3Separation Physical isolation that satisfies offline copy requirements
- 4Jurisdiction Stored where your regulatory position requires
Related Reading
You may also find these useful
Protecting Students, Peers and Partners: A Practical Education Data Briefing
A practical, forward-looking briefing to help schools, colleges and universities protect students, staff and partner data after the Department for Education breach.
Urgent Briefing and Advice: Protecting Personal Data for High-Profile Figures in the Public Eye
Practical steps for serving and former politicians, councillors, campaigners, journalists, executives, broadcasters and anyone in the public eye, covering email security, device hygiene, threat handling and offline secure storage.
500,000 Volunteers Breached Through Authorised Access: A Controlled Access Buyer's Guide
In April 2026, approved researchers exfiltrated the health records, genetic data, and medical histories of 500,000 UK Biobank volunteers through authorised access channels, then listed the data for sale on Alibaba. The breach was not caused by a hack. It was caused by a model that assumes licence agreements can prevent data theft. This guide covers why that model fails and what physical controls replace it.
Put this guide into practice
Ready to apply what you have learned? Explore how Control by Firevault governs the physical paths into your systems.
From £360 a month including VAT. 36-month commitment. First payment at checkout.
Business
Size your Vault.
2TB, 4TB or 8TB of dedicated hardware, from £360 a month inc VAT.
Larger estates
Request a Storage design.
From 20TB, designed with our solutions team.
Personal
LUV, 300GB.
Identity documents, wills and family archives, opened one day a week.