Firevault, offline secure storage, physically disconnected from the internet
Pricing

Vault product iconCompliance · NIS2
NIS2 compliance with Offline Secure Storage®.

NIS2 requires operational resilience from essential and important entities. Offline Secure Storage® adds physical disconnection as a resilience measure, so recovery does not depend on the network an incident has reached.

  • Supply-chain compromise
  • Ransomware on essential services
  • Failure to notify
  • Business-continuity breakdown

As featured in

  • TechRadar Pro logo
  • Yahoo Finance logo
  • Channel Insider logo
  • Security Buyer logo
  • SecurityBrief logo

The reality

NIS2 raised the bar because incidents like these kept landing.

Each incident below disrupted an organisation that regulators would now class as essential or important. In every case, the data that mattered was reachable from a connected network when the attackers arrived.

  1. NIS2 expects continuity under attack. A recovery copy on physically disconnected hardware is still there when the connected estate is not.

  2. Management is personally accountable under NIS2. Out-of-band authorisation and logged, time-bounded sessions give boards something concrete to stand behind.

  3. Records held offline cannot be reached through a compromised supplier connection, because there is no connection to compromise.

Incident 1

Jaguar Land Rover: about £1.9bn.

A cyber attack halted production at JLR factories in September 2025. The Cyber Monitoring Centre put the cost to the UK economy at about £1.9 billion, with over 5,000 organisations affected.

Answered byGold copies stay disconnected

Incident 2

Synnovis: London hospitals disrupted.

A ransomware attack on pathology provider Synnovis led to 10,001 outpatient appointments and 1,680 elective procedures being postponed at two London trusts, and stolen data was published online. NHS England, 2024.

Answered byA full audit trail

Incident 3

M&S: online orders paused for 46 days.

Attackers reached Marks and Spencer systems through a third party in spring 2025. Online orders were paused for 46 days, with an expected hit to profit of about £300 million.

Answered bySelf-contained infrastructure

How OSS helps

Physical continuity
for essential services.

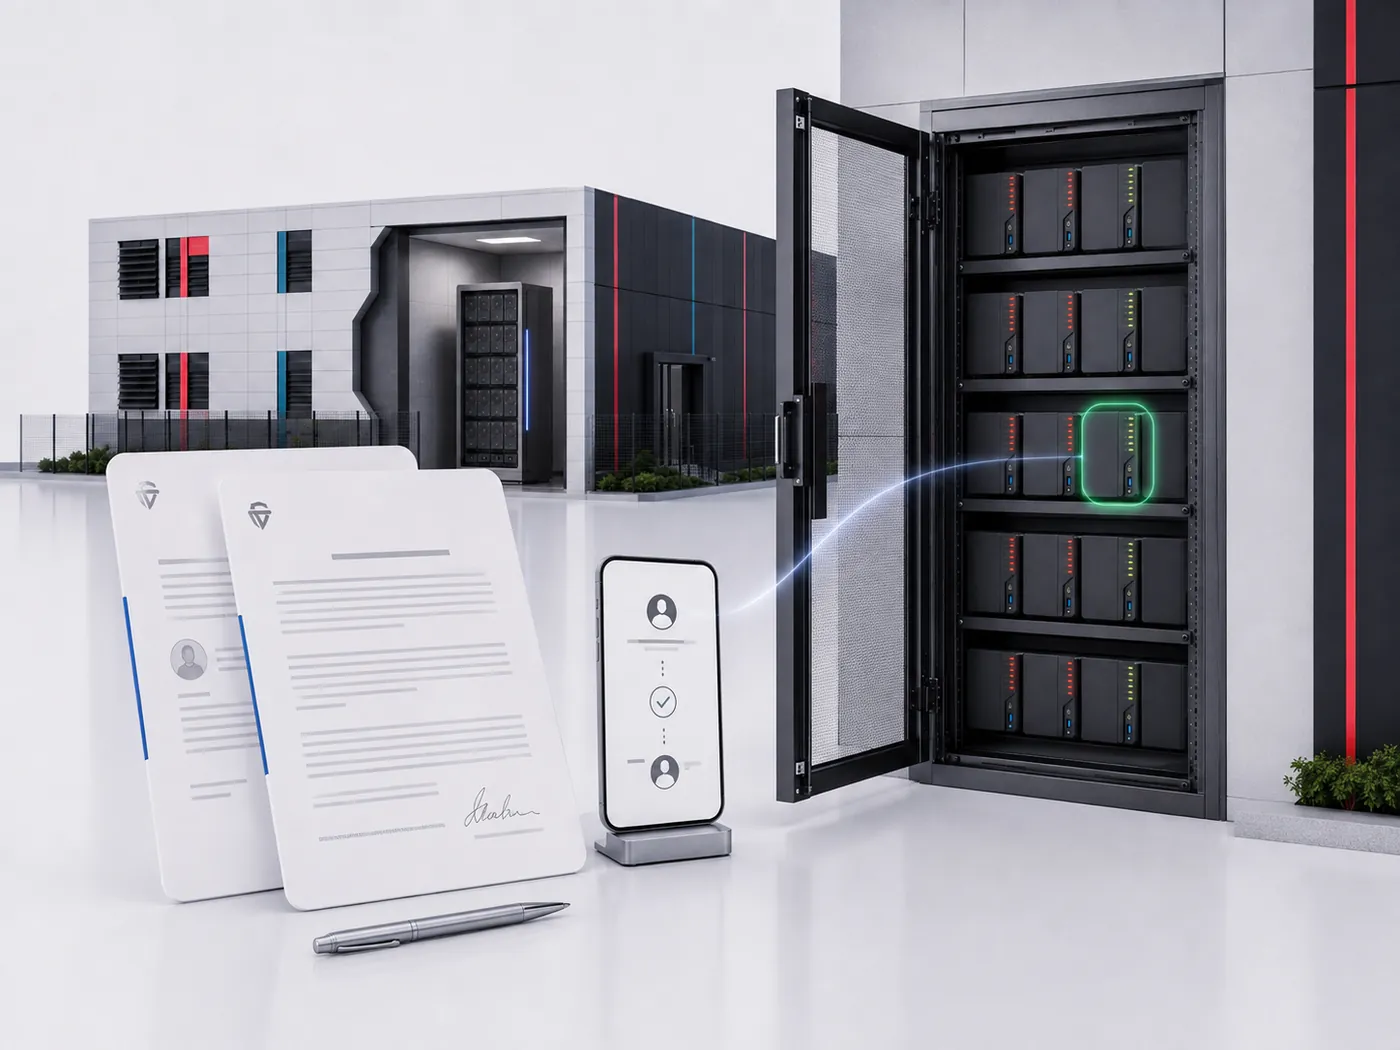
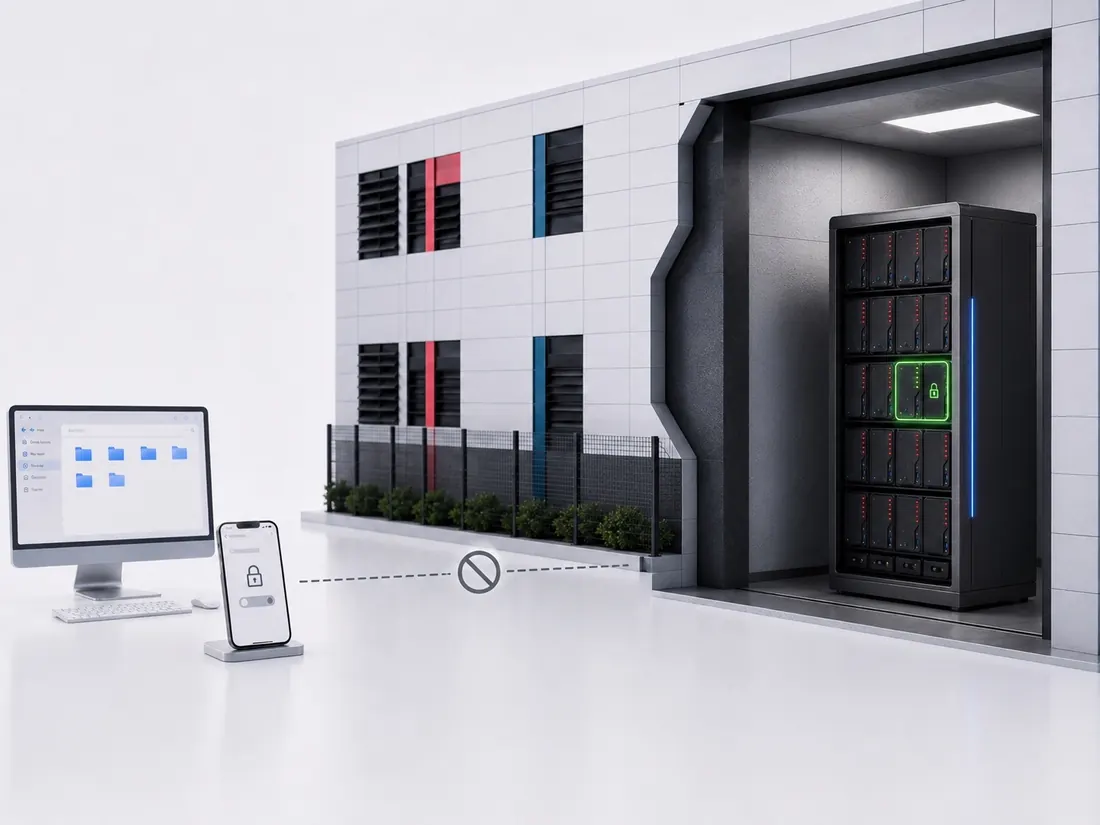
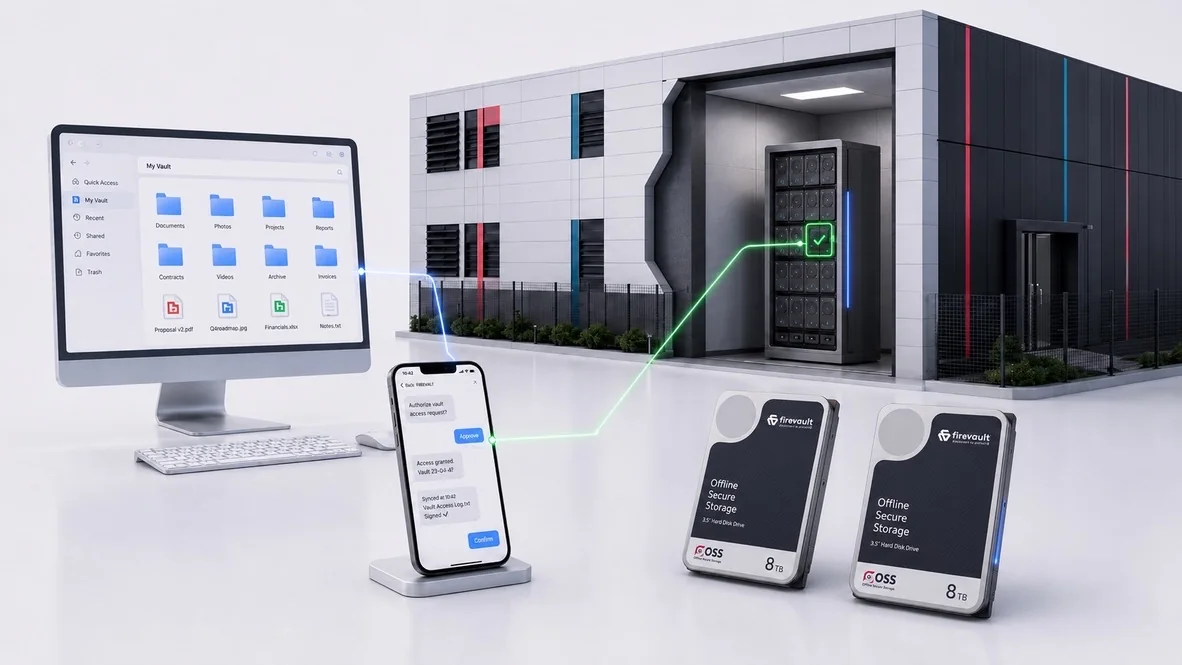
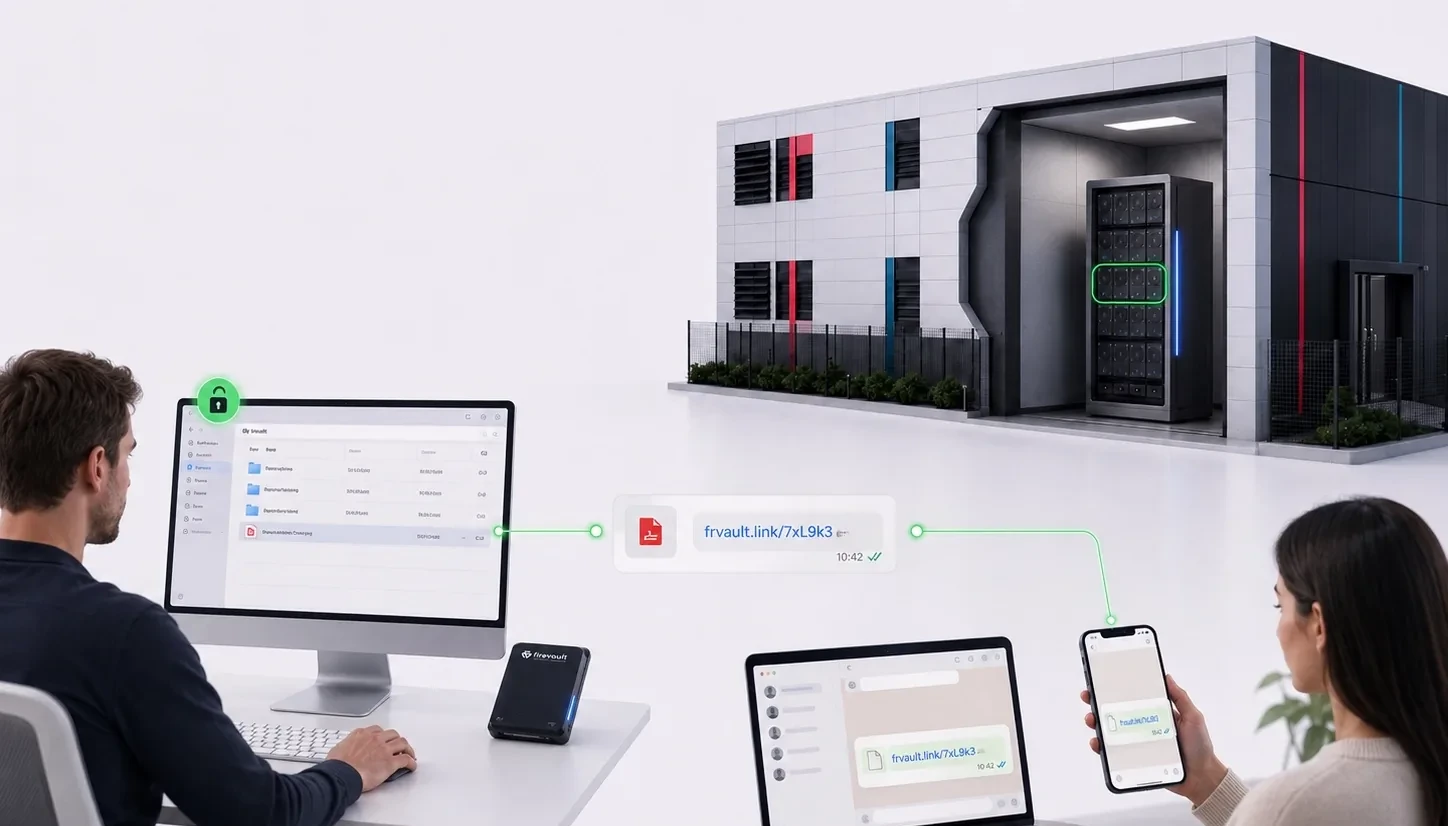
Critical records and recovery copies are written to dedicated RAID 1 drives inside a Firevault Bunker, held with no network connection while closed. Access is authorised out of band from a registered phone, a physical connection is created for the session, and the drives disconnect when it ends.

Step 1 of 3

Remove

Operational data and gold copies are taken off connected infrastructure and written to dedicated RAID 1 drives inside a Firevault Bunker.

No cloud. No shared portal.

Where the records are
Dedicated RAID 1 drives
Live network
No longer holds the archive
Access
Identity-checked

Illustration.

CAF-aligned

Supporting NIS2 obligations, not certifying against them.

Firevault is not a NIS2 auditor and OSS is not a certified NIS2 product. It is a physical control that supports the risk management, business continuity and incident handling measures the directive requires. Full mapping detail is available on request.

Offline Secure Storage® and CAF

Objectives B and D

Physically disconnected gold copies support B3 Data Security, B5 Resilient Networks and Systems, and D1 Response and Recovery Planning.

How OSS works

Control Blueprints and CAF

Objectives A and C

Identity-verified access, session logging and separation of operational and archived data support A2 Risk Management, A4 Supply Chain and C1 Security Monitoring.

See Control Blueprints

Firebreak® and CAF

Objective B at the OT boundary

Physical-layer OT/IT separation supports B2 Identity and Access Control, B4 System Security, and B5 Resilient Networks and Systems.

Explore Firebreak®

The products

Which Offline Secure Storage® fits essential and important entities?

Every tier is the same physical principle at a different scale. Choose the access pattern that matches your continuity plan and the teams who execute it.

Vault

On-demand access, 24/7, to a digital safe deposit box. 2TB, 4TB or 8TB, from £360 a month inc VAT.

LUV

Deep cold storage for gold copies, runbooks and incident evidence accessed periodically. 300GB, with one nominated access day each week within a 12-hour window. £74.99 a month inc VAT, 36-month commitment.

Storage

Scalable offline capacity from 20TB upwards, designed with the solutions team around your requirement.

Vault

Physically offline between sessions.

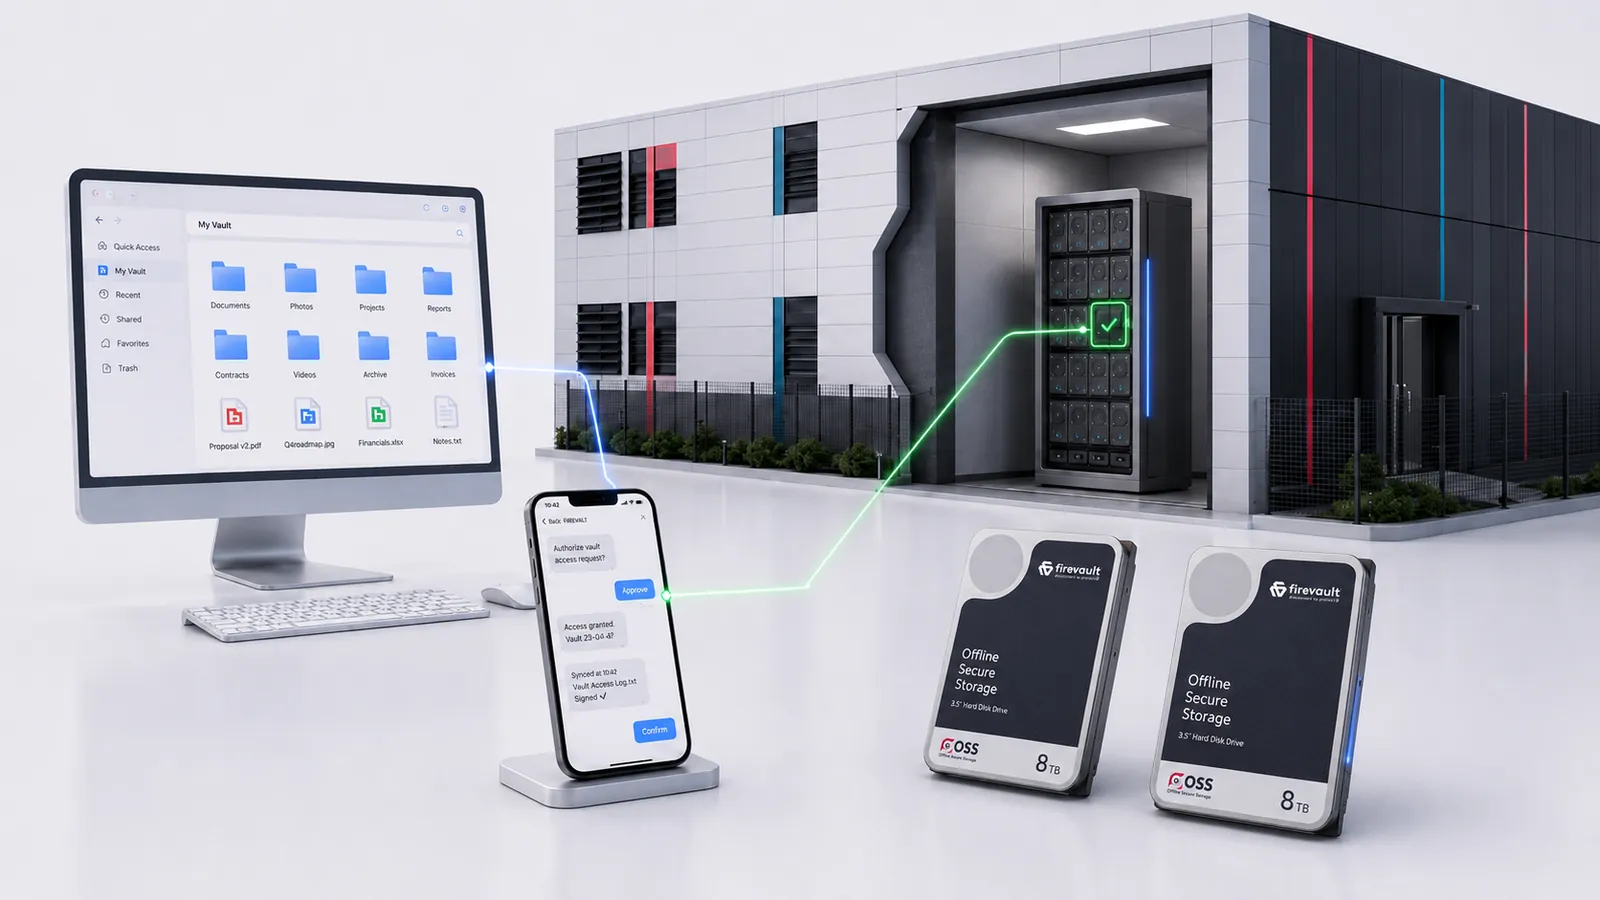
Opening a Vault: files on a desktop, approval on a phone, and the Vault held in a separate, secure Firevault Bunker

Open a session

Ask from your registered phone and confirm it is you.

A session requested from a phone while files open on a desktop

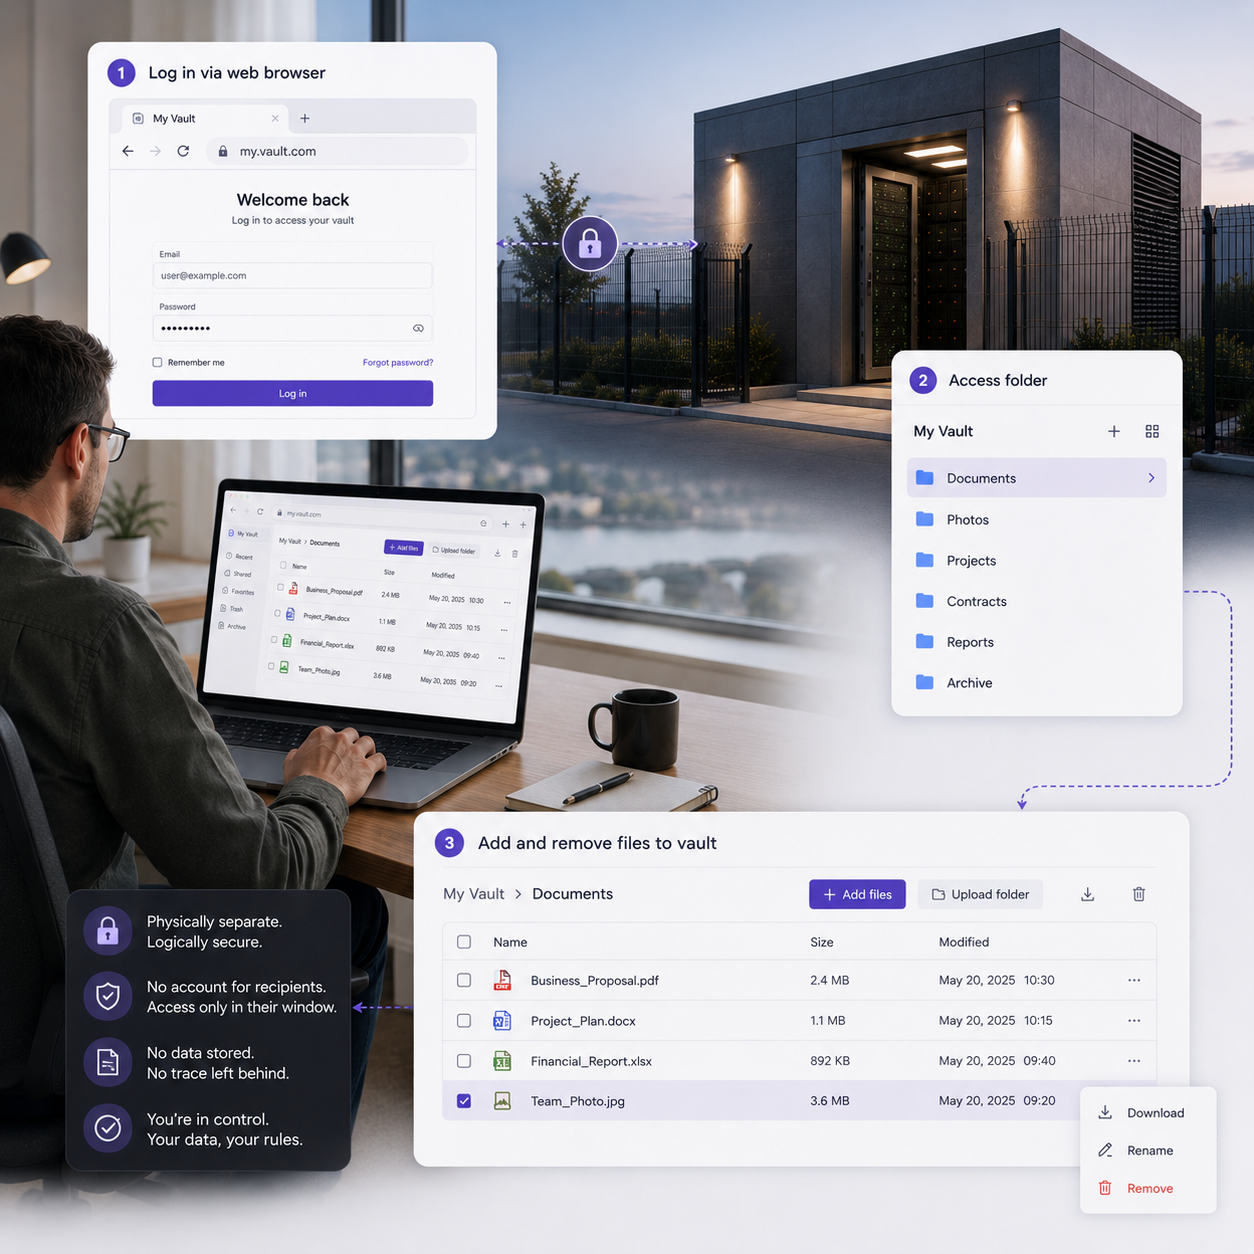
File Manager

Work with your files for up to 120 minutes.

File Manager in the browser during an authorised OSS session

LUV

Opens on a day you choose each week, for 12 hours.

Storage

From 20TB, growing in 20TB steps.

Use cases for NIS2 sectors

What regulated entities take offline first.

The records your continuity plan cannot function without, and the ones an attacker would most like to reach.

Recovery

Gold copies of critical systems

Plans

Continuity and incident runbooks

Evidence

Incident and notification records

Supply chain

Supplier and contract records

Governance

Board decisions on cyber risk

How to get started

From discovery call to go-live.

  1. 1

    Discovery call

    Understand what you need to protect and how you operate.

  2. 2

    Vault configuration

    Select your tier, capacity and access model.

  3. 3

    Identity verification

    Complete KYC/AML and set up multi-factor authentication.

  4. 4

    Go live

    Data ingestion, access policy activation and ongoing support.

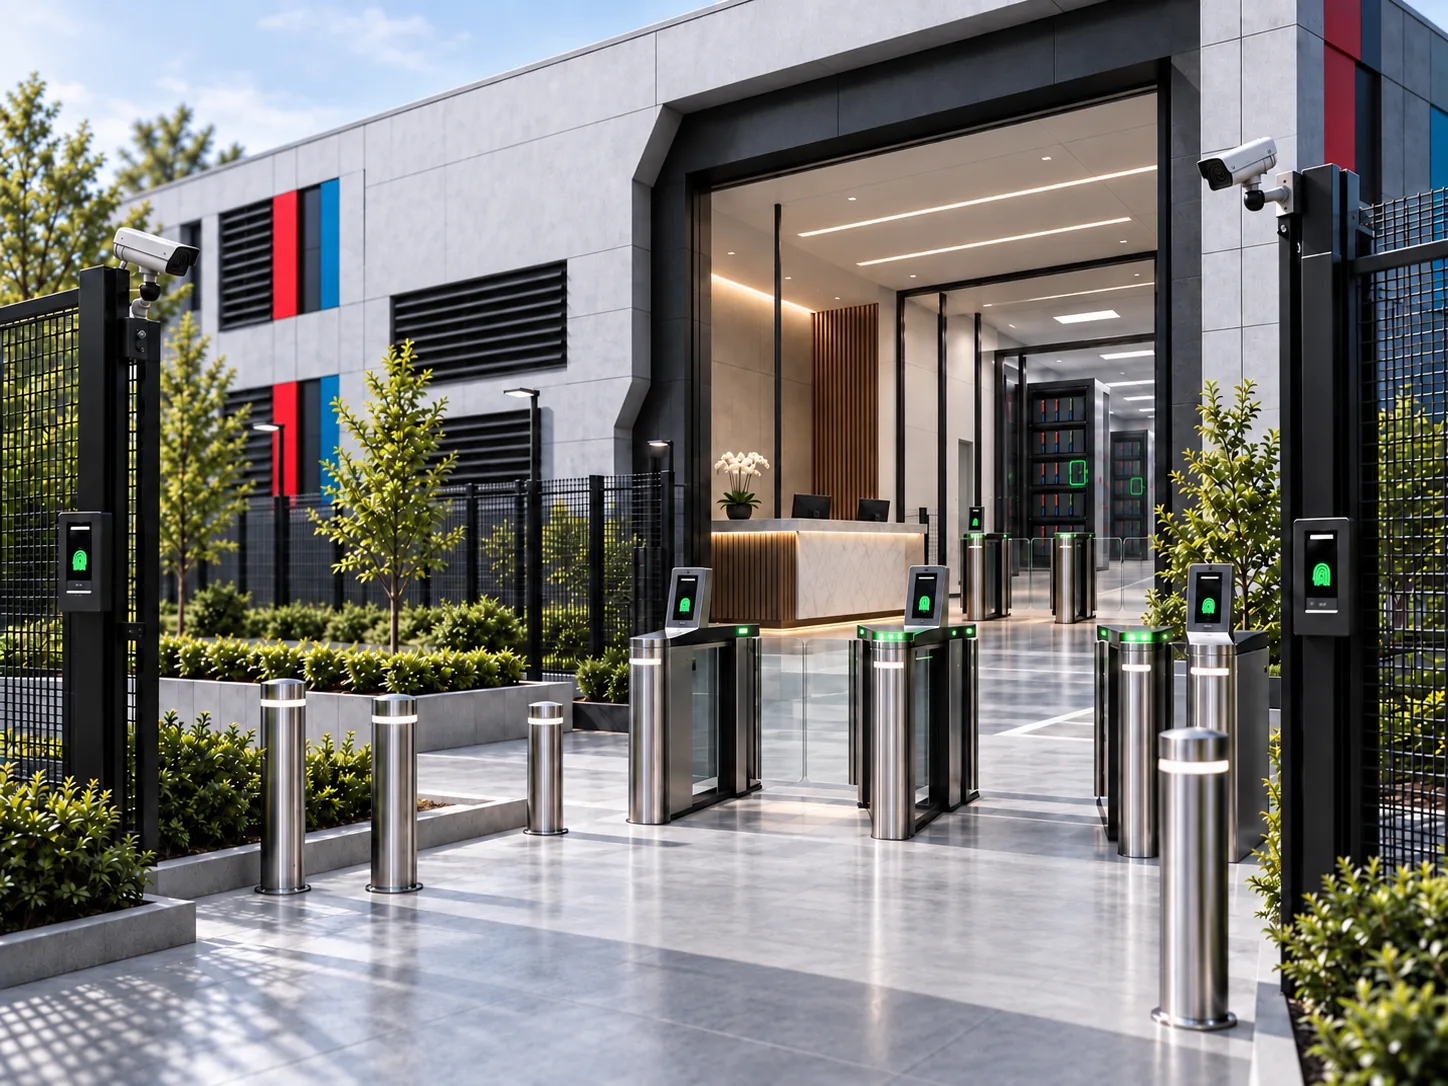
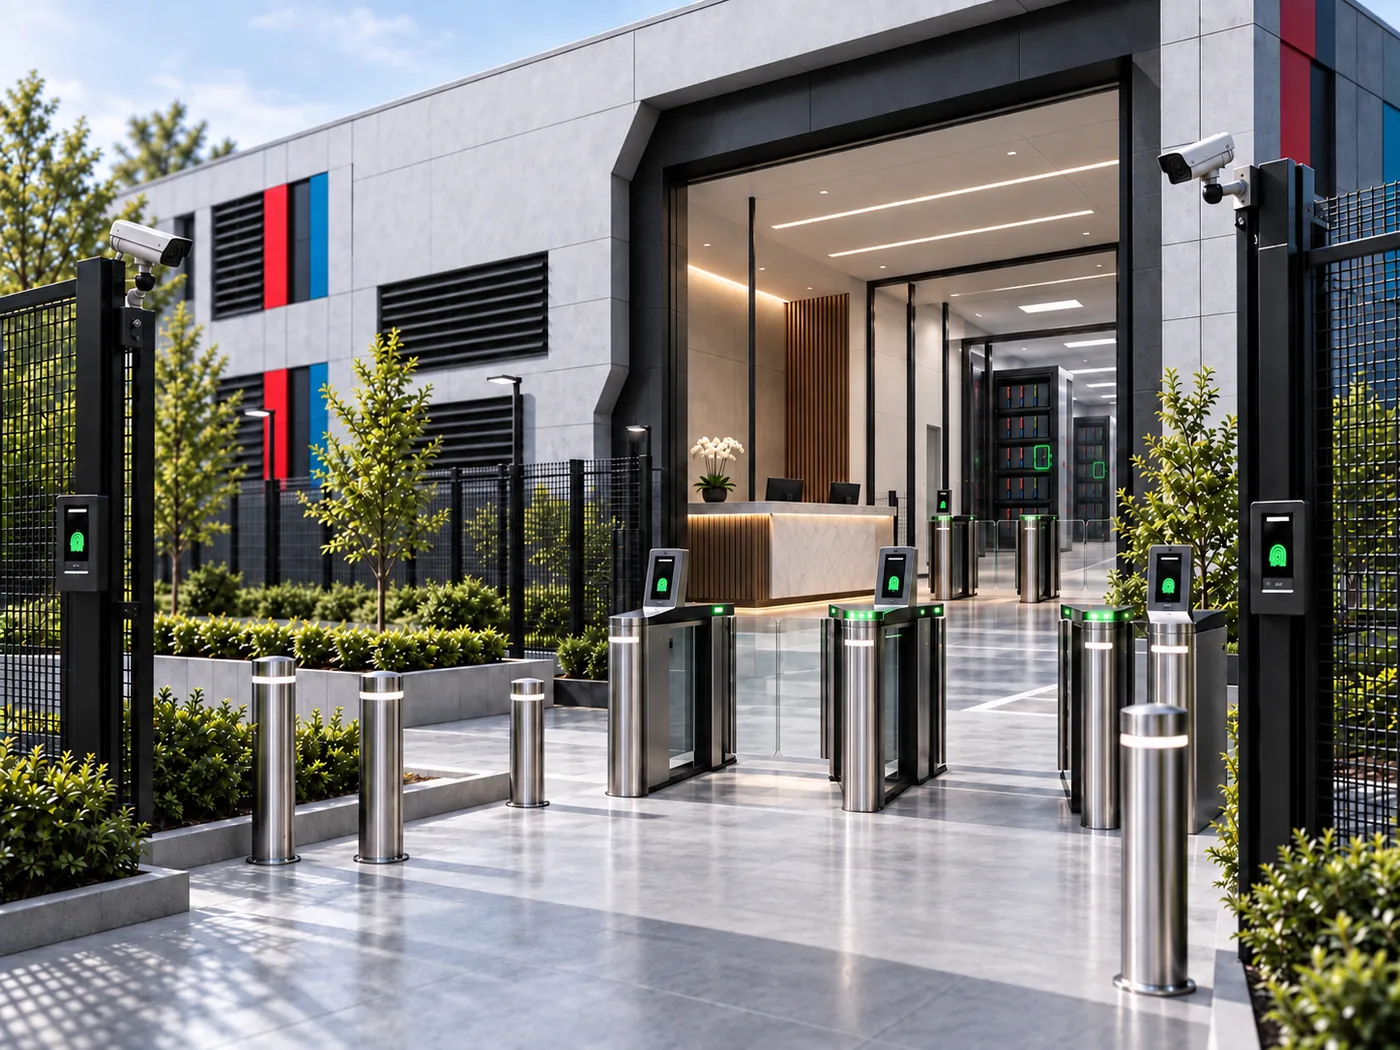
Secured Firevault Bunker entrance with biometric entry and monitored access

Every Offline Secure Storage® instance is built on the same four physical principles.

Continuity the hardware guarantees.

Every Offline Secure Storage® instance is built on the same four physical principles.

  • Physical storage

    Offline Secure Storage instances are held on dedicated physical hard drives, not in S3 cloud buckets, shared storage pools or multi-tenant infrastructure. Your selected data is assigned to real hardware, with dedicated RAID 1 drives providing resilience.

    Explore physical storage
  • Physical ownership

    Each Offline Secure Storage instance is allocated to a specific customer, with dedicated physical capacity and clearly defined ownership. Your data is not pooled, commingled or held within a shared storage estate.

    Explore physical ownership
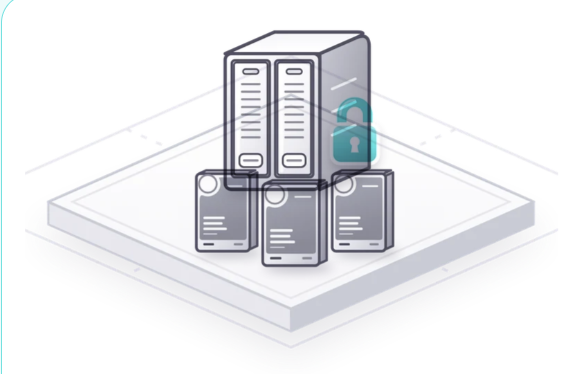
  • Physically disconnected Offline Secure Storage: server, three drives and a padlock

    Physical control

    Access begins outside the normal network path. An authorised out-of-band command, such as SMS, controls the physical Layer 1 connection to your #OSS instance. When access is not required, that network path is physically disconnected.

    Explore physical control
  • Physical security

    Your #OSS hardware is housed in carefully selected, professionally managed data centres with layered physical security, resilient power and environmental controls. Access is tightly controlled using three-factor authentication, including biometric identification, supported by 24/7 monitoring, restricted access zones and a complete audit trail.

    Explore physical security

Questions

What regulated entities ask first

NIS2 requires measures for business continuity and crisis management. OSS holds recovery copies on dedicated hardware that is physically disconnected between sessions, so the copy your continuity plan depends on cannot be encrypted or deleted through the network during an incident.

Yes. Records held offline are unreachable through compromised supplier accounts or third-party connections, because the hardware has no network path while it is closed.

On dedicated hardware in a secure Firevault Bunker. For security, we do not publish Bunker locations.

With a Vault, request a session at any time, 24/7, from your registered phone, sign in with your credentials and MFA, and work in File Share during a session of up to 120 minutes. LUV opens on your nominated access day each week, for 12 hours.

All questions about OSS

Hold the recovery copy where the incident cannot reach.

LUV from £74.99 and Vault from £360 a month, including VAT. 36-month commitment, first payment at checkout.