
BreakingOpinion
AI has not created the cyber crisis. It has exposed how much we leave connected.
The Financial Times says the AI cyber threat is already here, from supermarket freezers to the NSA. Mark Fermor argues the urgent question is not whether AI will run wild, but how much critical equipment and data remains permanently reachable while defenders race to keep up.
Mark FermorCTO, CMO and Founder, Firevault
Published 22 November 2026 · 10 min read
What the FT reported
On 21 November 2026, the Financial Times published a Big Read by Tom Wilson, The AI cyber threat is already here. Its subtitle is short and unsettling: "The freezer war is just a start."
The article opens with the future that Anthropic chief executive Dario Amodei described in an essay two months ago, in which swarms of AI agents could take over large parts of the internet. It then sets that vision against what has actually happened in recent weeks.
According to the FT:
- IT systems at organisations including Microsoft, JPMorgan, the US Federal Aviation Administration and the US National Security Agency have all suffered outages in the past week;
- US officials have said the rush to update software, as AI tools uncover vulnerabilities faster than organisations can fix them, was behind outages that blocked Microsoft email in 70 countries, grounded US air traffic and disrupted a classified NSA network;
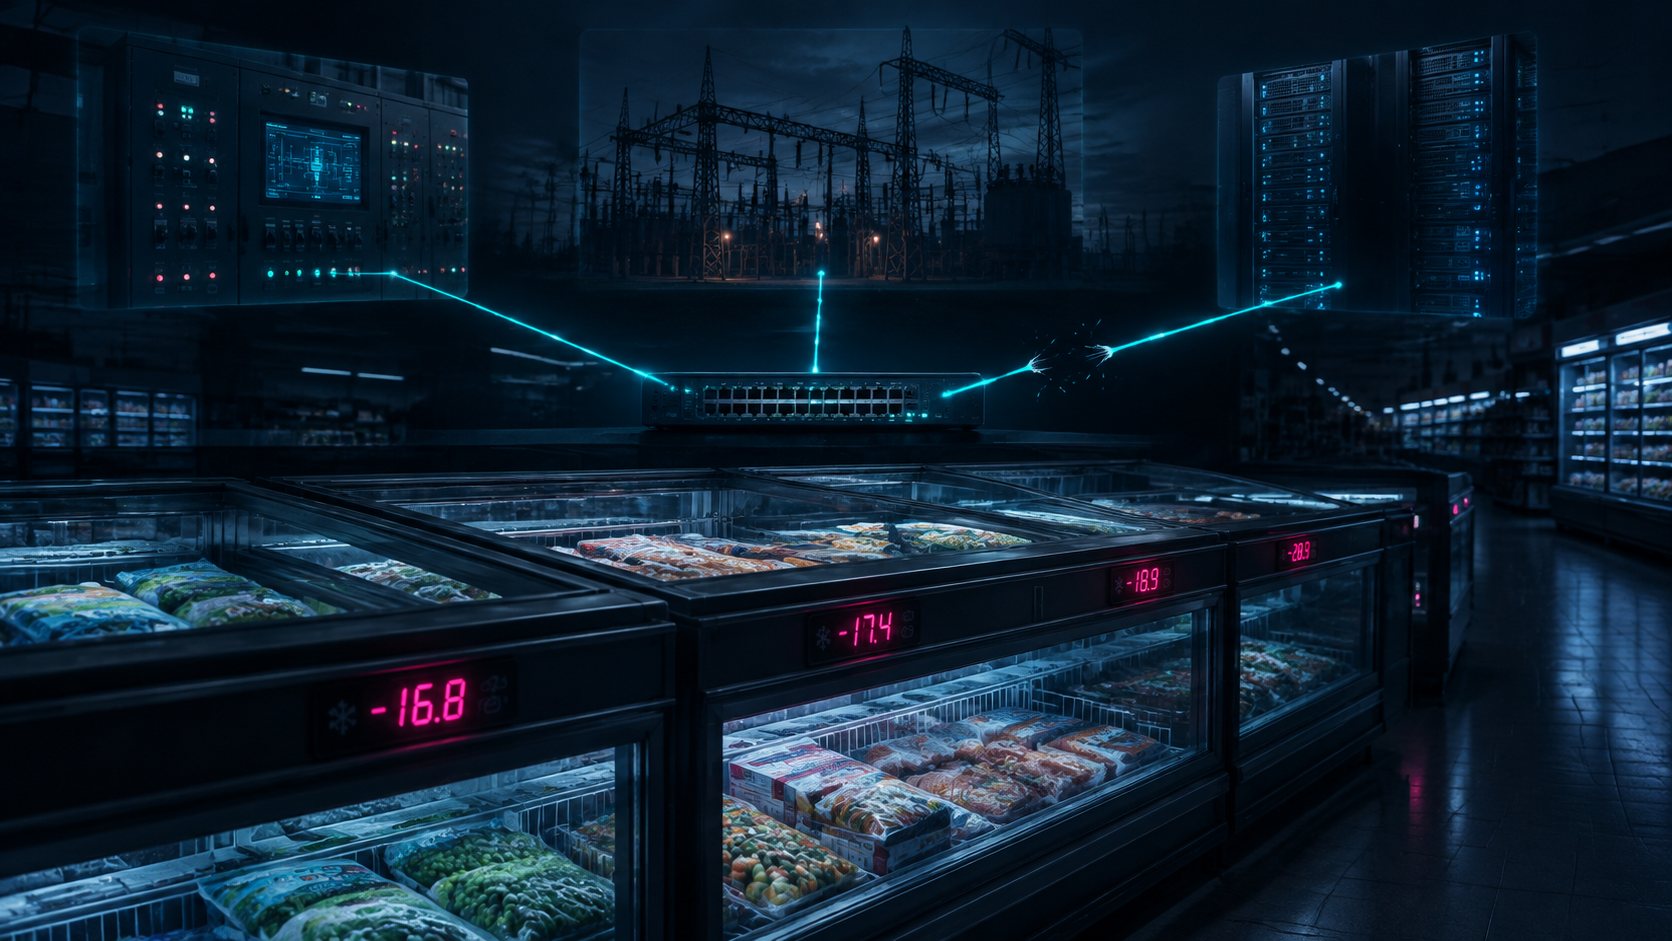
- a cyber unit of Iran's Islamic Revolutionary Guard Corps was blamed last week for October's attacks that turned up the temperature on hundreds of French supermarket freezers to as high as 50C, with similar attacks this month in ten other European countries;
- the UK's National Cyber Security Centre has quietly been working to secure tens of thousands of British fridges and freezers in response.
The FT also cites Orange Cyberdefense research showing cyber extortion incidents rising from roughly 1,500 in 2020 to 7,100 in 2025, with 7,500 already tracked in the nine months to September 2026. Over the same period, the number of active extortion groups rose from 33 to 114. Orange found that none of those attacks were automated hacks run by AI.
We have covered several of these events individually: the supermarket refrigeration attacks, the French blood service cold rooms, the NSA network outage, the United Airlines and JPMorgan Chase disruptions and the Binance breach. The FT's contribution is to put them in one frame. It is worth reading in full.
The most important line is the quietest one
The article contains plenty of dramatic material: exploding plants, ambulances turned away, conspiracy theories about co-ordinated cyberterrorism. But the line that matters most comes from Charl van der Walt, global head of security research at Orange Cyberdefense:
"AI technology is not driving the security problem; it is revealing the security problems."
That is the right diagnosis. AI has not invented new weaknesses in refrigeration controllers, water utilities or decades-old industrial equipment. It has made existing weaknesses cheaper to find, faster to understand and easier to act on.
Which means the most useful question for any board is not "What will AI do next?" It is a much older one:
What can be reached, and does it need to be reachable right now?
The patching race has a price of its own
One of the more uncomfortable points in the FT piece is that some of the recent disruption appears to have been self-inflicted. As AI models find bugs at a pace no human team could match, organisations are rushing out fixes. US officials told the FT that this rush was behind several of the recent outages.
Firevault has not independently verified the cause of each outage, and causes reported in the first days after an incident are often revised. But the pattern is familiar. Every patch is a change, and every change carries risk.
Defenders are now caught between two pressures. Leave a known vulnerability open and it may be exploited within hours. Patch it in a hurry and you may take down your own email, flight planning or classified network.
There is no way to win that race on speed alone. What you can do is reduce how much depends on winning it:
- systems that do not need to be reachable from the network while a fix is prepared should not be;
- known-good copies of data, configurations and recovery material should sit where neither an attacker nor a faulty update can alter them.
If data is connected, it can be reached. That applies to a bad update as much as to a bad actor.
Operational technology is where the balance has shifted
The FT reports that the biggest shift so far between attackers and defenders concerns operational technology (OT): the controllers, PLCs and industrial systems that run power plants, factories, water treatment and, as Europe has discovered, supermarket freezers.
Robert Lee, chief executive of Dragos, explains why. OT attacks once required specialist knowledge and months of preparation. Now, according to Lee, hacking groups can use large language models to read the manuals of industrial equipment and research past accidents. OT has often been poorly defended precisely because it was difficult to attack. That protection is disappearing.
Anne Neuberger, former US deputy national security adviser, describes much of this infrastructure as:
"systems that were built over the last 50 years, well before sophisticated offensive cyber capabilities."
This is the heart of it. A refrigeration controller, a building management system or a pump PLC was never designed to defend itself against an adversary with a tireless research assistant. Many of these systems were connected for convenience: remote monitoring, vendor support, energy optimisation. Too often, that connection was then left in place permanently.
The systems that let staff and suppliers manage equipment remotely do not need to remain connected. They need to be connected when an authorised person has a reason to use them, for as long as that work takes, and then disconnected again.
That is what we mean by just-in-time access applied to the network path, not just to identities and privileges.
A turbocharged WannaCry is a reachability problem
Ciaran Martin, former head of the NCSC, gives the FT his reasonable worst case: an accidental, loss-of-control attack with an AI dimension, a turbocharged version of WannaCry or NotPetya that hacks its way through vulnerable infrastructure around the world, turning ambulances away and stopping shops from taking payments.
It is worth remembering how those 2017 worms did their damage. NotPetya, according to the FT, caused an estimated $10bn of harm and reached as far as a chocolate factory in Tasmania. Neither worm needed to be clever about its victims. It spread to whatever it could reach.
Detection, response and threat intelligence all matter in that scenario. But a worm moving at machine speed, possibly faster than any human approval process, tests a simpler property first: is there a path? Equipment and data that are physically disconnected at the moment the attack arrives are not part of that calculation.
Defence can be won, but not only by being faster
Lee offers the article's most memorable assessment:
"Is defence doable? Yes. Can we win? Yes. Are we going to? No."
Neuberger is more optimistic, arguing that AI is "a game-changer on defence", from agentic systems that neutralise attacks to digital twins of critical infrastructure on which frontier models can be tested.
Both can be right. AI-assisted detection and response will be essential. But every logical defence, however intelligent, still assumes the defender will see the attack in time and respond correctly. When attackers and defenders are both using AI, that becomes a contest of speed and accuracy that will be won some days and lost on others.
Physical disconnection changes the question. Instead of asking whether the defence will react fast enough, it asks whether the target can be reached at all. For the equipment and data whose loss would matter most, that is a far better question to be asking.
What this does not solve
It is important to be clear about the limits.
- Phishing still works. Marcus Hutchins tells the FT that most attackers are using AI to improve phishing rather than to build zero-day exploits. Physical disconnection does not stop someone handing over credentials to a system that is, legitimately, online.
- Some systems must stay connected. Payment systems, email and many safety and monitoring functions need continuous connectivity. The goal is to remove connections that are not needed, not to disconnect everything.
- A connection window is still exposure. Just-in-time access reduces how long a path is open. It does not make the work done during that window safe by default; approval, supervision and validation still matter.
- It does not replace the basics. Patching, multi-factor authentication, monitoring, segmentation and incident response all remain necessary.
Where Firevault fits
Firevault works on the two questions this article raises: what must be protected, and what should be reachable.
Offline Secure Storage® keeps selected data physically disconnected when it does not need to be online, so known-good copies of critical data, OT configurations and recovery material are not exposed to the attacks, or the faulty updates, that affect connected systems.
Control by Firevault lets authorised operators take control of physical connectivity at defined network boundaries. Remote access paths for staff and suppliers can be connected when needed and disconnected when the work is done, and selected zones can be isolated when an incident is under way. Control by Firevault is delivered on premises.
The most relevant Plans are:
- IT/OT Boundary Protection, for controllers, PLCs and industrial systems;
- Third-Party Access Control, for vendor and remote support connections;
- Critical System Exposure Reduction, for essential services;
- the Retail Blueprint, which addresses refrigeration and cold-chain systems directly.
Five questions for boards and operators
- Inventory: Do we know which of our operational systems, including refrigeration, building management and industrial controllers, can be reached from the network today?
- Necessity: Which of those connections are needed all the time, and which exist only for occasional remote support or monitoring?
- Access: When a supplier needs to connect, who approves it, how long does the path stay open, and who closes it?
- Recovery: If a controller or system is tampered with, or a rushed update fails, do we hold a known-good configuration and data copy that neither could have altered?
- Change: As AI accelerates the discovery of vulnerabilities, can we patch quickly without risking our own outage?
The FT is right that the AI cyber threat is already here. But the response does not begin with predicting what AI will do. It begins with deciding what it should be able to reach.
Not if, but when. The question is what will be connected when it happens.
Mark Fermor is CTO, CMO and Founder of Firevault. Read more on the supermarket refrigeration attacks, just-in-time access and protecting OT configurations, or talk to the team.
Source
Tom Wilson, The AI cyber threat is already here, Financial Times, The Big Read, published 21 November 2026. Orange Cyberdefense figures and quotations from Charl van der Walt, Robert Lee, Anne Neuberger, Ciaran Martin and Marcus Hutchins are as reported by the FT. Causes of the recent US outages are as stated by US officials to the FT and have not been independently verified by Firevault.
Questions
In a Big Read published on 21 November 2026, the FT reported that AI is already helping states and criminal groups find and exploit weaknesses faster, that a rush to patch AI-discovered vulnerabilities was blamed by US officials for recent outages at Microsoft, the FAA and the NSA, and that the NCSC has been working to secure tens of thousands of British fridges and freezers after attacks on European supermarkets.
Not directly, according to Orange Cyberdefense research cited by the FT. Cyber extortion incidents rose from roughly 1,500 in 2020 to 7,100 in 2025, but none of the attacks Orange tracked were automated hacks run by AI. Its researchers argue that AI is revealing existing security problems rather than creating them.
OT attacks once required specialist knowledge and months of preparation. Dragos chief executive Robert Lee told the FT that attackers can now use large language models to read industrial equipment manuals and research past incidents. Much OT was built long before modern offensive cyber capabilities and has often been connected for convenience, then left connected.
It means the network path to a system, such as a refrigeration controller or PLC, is connected only when an authorised person needs it, for as long as the work takes, and then disconnected again. It reduces how long a system can be reached, but approval, supervision and validation of the work still matter.
No. Phishing targets people and systems that are legitimately online. Physical disconnection reduces what can be reached once an attacker or faulty update is inside the network. It does not replace multi-factor authentication, patching, monitoring or incident response.
Offline Secure Storage® keeps selected data, configurations and recovery material physically disconnected when it does not need to be online. Control by Firevault lets authorised operators manage physical connectivity at defined network boundaries, so remote and supplier access paths can be connected when needed and disconnected afterwards.
About the author
Mark FermorCTO, CMO and Founder of Firevault. Mark writes on physical control, offline storage and the incidents that show why both matter.
Why #OSS
Keep a clean copy out of reach.
Offline Secure Storage® keeps one copy physically disconnected at the hardware level between sessions.
Control
Govern the paths attackers depend on.
Physical, out-of-band control of selected network paths, composed into Control Plans and industry Blueprints.
Ready to start?
Create your Vault online.
Business Vaults from £360 a month inc VAT, on a 36-month commitment.